 Menu
On this page
- What IT Audit Companies Actually Do
- Types of IT Audits
- Key Criteria for Evaluating IT Audit Firms
- Benchmarking Audit Costs and Timelines
- The Main Categories of IT Audit Firms
- Is a Big Four firm better than a specialist for a SOC 2 audit?
- How do I choose an IT audit company?
- Your Top Questions About Choosing an Auditor, Answered
SOC 1, SOC 2 and SOC 3 reports must be signed by a licensed CPA firm, ISO 27001 certificates come from an accredited certification body, and PCI DSS assessments come from a Qualified Security Assessor. Our directory lists 192 audit firms: 19 Big Four member firms, 107 other full-service CPA firms, and 66 assurance specialists. Of those firms, 21 also issue ISO 27001 certificates as accredited certification bodies. Updated October 6, 2026.
As of October 6, 2026, Big Four member firms list Type 2 starting estimates from $45,000 to $80,000, and assurance specialists list them from $2,500 to $50,000. These are directory estimates, not quotes.
Big Four member firms list a median Type 2 starting estimate of $65,000, against $30,000 for full-service CPA firms and $15,500 for assurance specialists.
A group median is a guide to the market, not to any one firm's quote: ask each finalist to price the same written scope.
- Big Four member firmsn = 19median $65,000
- Full-service CPA firmsn = 107median $30,000
- Assurance specialistsn = 66median $15,500
IT audit companies are independent firms that examine your information systems, controls, and security practices against a recognized standard, then issue a formal report on what they found. The work spans SOC 1 and SOC 2 reports, ISO 27001 certification, PCI DSS assessments, HIPAA and HITRUST reviews, internal IT control testing, and broader cybersecurity audits. Which firm fits depends on the standard you need, your industry, and whether the firm carries the right accreditation to sign the report you’re buying.
Most companies arrive here because a customer, regulator, or board asked for proof. The same engagement that satisfies that request can also surface weaknesses before they become incidents. This guide covers what these firms do, the main types of IT audits, how the firms differ, what engagements cost, and how to choose one without overpaying for a name. If SOC 2 is the engagement you need, the best SOC 2 auditors, compared is where to compare CPA firms.
What IT Audit Companies Actually Do
At their core, IT audit companies are independent validators. They measure your organization’s controls against an established framework and issue a report or attestation on whether those controls are designed and operating as intended. They confirm you actually do what your policies say you do.
That independence is the whole point. For an attestation report like SOC 2 to carry weight, the firm signing it cannot also be the firm that built your controls, a line that AICPA standards enforce strictly. The same principle applies to ISO 27001 certification bodies and PCI Qualified Security Assessors (QSAs): the assessor must be accredited and arm’s-length.
For technology vendors, that report is often a sales requirement. Many enterprise and regulated buyers ask for one early in procurement, and a clean report can answer many security questionnaire questions in advance.
Types of IT Audits
“IT audit” is an umbrella term. Before you shortlist firms, get specific about which engagement you actually need, because not every firm is accredited to deliver all of them.
- SOC 2 (and SOC 1, SOC 3): Attestation reports against the AICPA’s Trust Services Criteria. SOC 2 is the default for SaaS and cloud vendors; SOC 1 covers controls relevant to clients’ financial reporting; SOC 3 is a public-facing summary. Only a licensed CPA firm can issue these. See our guide to SOC 2 audit firms for how to compare them.
- ISO 27001 certification: A management-system audit against an international standard, issued by an accredited certification body rather than a CPA firm. Common when you sell internationally.
- PCI DSS assessment: Required if you store, process, or transmit cardholder data. Performed by a Qualified Security Assessor (QSA) for larger merchants and service providers.
- HIPAA and HITRUST: Healthcare-focused reviews. HITRUST CSF certification, in particular, is run by HITRUST-authorized assessor firms.
- Internal IT controls and IT general controls (ITGC): Reviews of access management, change management, and operations, often as part of a financial-statement audit or SOX program for public companies and financial institutions.
- Cybersecurity and penetration testing: Technical assessments of your defenses, sometimes bundled with a compliance audit. Our overview of cybersecurity audit companies breaks down where these overlap with SOC 2.
A single firm may cover several of these, but accreditation matters: a CPA firm can sign a SOC 2 report; a certification body issues your ISO 27001 certificate; a QSA validates PCI DSS. Match the firm’s credentials to the deliverable you need.
Readiness vs. the Audit Itself
Across all of these, firms also offer readiness assessments, a structured dry run that finds and helps you fix control gaps before the formal engagement starts. A readiness assessment is consultative; the audit is the independent examination. To preserve independence, the firm that signs your attestation generally cannot have built the controls it’s testing, so larger engagements often split readiness and audit between separate providers. Our guide to SOC 2 compliance consultants explains where the consultant’s role ends and the auditor’s begins.
Key Criteria for Evaluating IT Audit Firms
The lowest price is not the only factor. A cheap auditor who misses key details, doesn’t understand your business, or delivers a confusing report can cause more headaches than they solve. You’ll waste time, frustrate your sales team, and potentially lose deals.
Look for a firm that understands both the compliance framework and your business. That means checking its industry experience, the technical depth of its team, how it communicates, and the tools it uses to make the audit process less painful.
Industry and Technical Expertise
An auditor’s experience in your industry (SaaS, FinTech, or HealthTech, for example) matters. A firm that already knows your world understands the common risks, customer expectations, and regulatory pressures you face, and can give relevant advice instead of generic recommendations.
The technical skill of the actual audit team matters just as much. You need people who can have an intelligent conversation with your engineers about your cloud setup, CI/CD pipeline, and security stack. If they don’t get your tech, they can’t audit it effectively.
Key questions to vet their expertise:
- Industry Focus: Can you share some anonymized case studies from companies similar to ours in size and sector?
- Technical Background: What’s the background of the auditors who will actually work on our account? Do they have real-world experience with our stack (AWS, GCP, Azure)?
- Credentials: Are the lead auditors Certified Public Accountants (CPAs)? Do they hold serious security certifications like CISA (Certified Information Systems Auditor) or CISSP (Certified Information Systems Security Professional)?
Accreditation, Peer Review, and Independence
This check is easy to skip, and a mismatch can invalidate your report. The credential has to match the deliverable:
- SOC 1/2/3: Must be signed by a licensed CPA firm. Reputable firms undergo an AICPA peer review every three years, a quality check by an outside CPA firm. Ask for the peer review status; it’s public and a fair firm will share it.
- ISO 27001: Your certificate should come from a body accredited under a recognized scheme (for example, an ANAB- or UKAS-accredited certification body). A “certificate” from an unaccredited assessor carries little weight with enterprise buyers.
- PCI DSS: The assessor should be a current Qualified Security Assessor (QSA) listed on the PCI Security Standards Council site.
Independence matters just as much as the credential. A firm cannot objectively audit controls it designed or implemented for you, so be cautious of “do it all” providers that bundle building your program with signing the report. If you want a deeper checklist, our SOC 2 auditor requirements guide lays out what a valid auditor must hold. Our guide to verifying a SOC 2 report helps you confirm a firm’s work is legitimate.
Audit Methodology and Tools
The firm’s process has a direct impact on your team’s workload and the project timeline. Firms that use specialized platforms for evidence collection and communication can put less administrative load on your team than firms that run on spreadsheets and email chains.
Look for a firm that emphasizes clear communication, transparent project tracking, and tools that reduce the administrative burden on your team.
Also look for specific framework knowledge. For SOC 2, an auditor with many SaaS engagements behind them is more likely to spot control gaps quickly. Ask about the assigned team’s expertise in SOC 2 compliance, and check the answers against our SOC 2 compliance checklist.
Communication and Report Clarity
The audit report is what you are paying for. A poorly written or confusing report can stall sales cycles and create friction with prospects. Always ask for a sanitized sample report to see how they present findings and structure their analysis.
Clear communication during the audit matters just as much. Good IT audit companies give you a dedicated point of contact, provide regular status updates, and have a clear process for answering questions. Radio silence from your auditor is a red flag that can lead to missed deadlines.
Before signing anything, get clarity on these points:
- Support Model: Will we have a dedicated project manager we can actually reach?
- Responsiveness: What are your guaranteed response times for questions during the audit?
- Reporting: Can we see a sample report to judge how you present findings and control effectiveness?
IT Audit Company Evaluation Checklist
Use this table to keep your evaluations of different firms consistent.
| Evaluation Criterion | Key Question To Ask | Why It Matters |
|---|---|---|
| Industry Experience | How many clients do you have in the SaaS/FinTech/HealthTech space? | Niche expertise means they understand your specific risks and business model, leading to a more relevant audit. |
| Technical Proficiency | What’s the technical background of the team assigned to us? | Your auditors need to speak the same language as your engineers to assess cloud environments and security tools effectively. |
| Audit Methodology | What platform do you use for evidence collection and project management? | Modern tools can save your team time compared to manual spreadsheet-and-email processes. |
| Responsiveness | What’s your average response time to client questions during an audit? | Slow communication delays projects. Aim for a same-day or 24-hour SLA. |
| Report Clarity | Can we see a sanitized sample report? | The final report is your primary deliverable. It must be clear, professional, and easy for your customers to understand. |
| Team Continuity | Will the same team handle our future surveillance audits? | High auditor turnover means you have to re-educate a new team every year, which is inefficient and costly. |
| Pricing Structure | Is your pricing fixed-fee? What are the common triggers for change orders? | Avoid surprises. A clear, all-inclusive price prevents scope creep and unexpected bills down the line. |
For a deeper dive into what to look for, our guide on selecting the right SOC 2 audit firm has more detailed questions to ask.
Benchmarking Audit Costs and Timelines
When you start looking at IT audit companies, two questions come up first: “How much is this going to cost?” and “How long is this going to take?”
You need realistic answers for budgeting, setting expectations with stakeholders, and planning compliance around your go-to-market schedule. The price and timeline for a SOC 2 audit vary widely, so start with what drives those numbers.
The big three factors are your company’s size, how complex your systems are, and which Trust Services Criteria (TSCs) you include in your scope. A 25-person startup with a simple tech stack is going to have a very different experience than a 300-person company juggling multiple cloud environments and intricate data flows.
Understanding SOC 2 Audit Pricing
Audit fees are anything but one-size-fits-all. A SOC 2 Type 1 audit, which is basically a snapshot that checks if your controls are designed correctly at a single point in time, is the cheaper option.
A SOC 2 Type 2 audit is a much deeper dive, and it costs more because of it. It tests whether those same controls are actually working effectively over a period of time, usually 6 to 12 months. Type 2 audits typically run 30 to 50% more than a Type 1 engagement.
Based on 2026 market rates, here is what you can realistically expect to pay for the audit fee alone:
| Company Stage | SOC 2 Type 1 (Audit Fee) | SOC 2 Type 2 (Audit Fee) |
|---|---|---|
| Early-stage startup (under 50 employees) | $7,500 to $20,000 | $15,000 to $35,000 |
| Growth-stage company (50 to 200 employees) | $15,000 to $35,000 | $30,000 to $60,000 |
| Mid-market or enterprise (200+ employees) | $30,000 to $60,000 | $50,000 to $150,000+ |
The audit fee is only one component. The total first-year investment, once you factor in readiness help, compliance software, penetration testing, and your team’s time, typically lands between $30,000 and $100,000 for most SaaS companies. Companies starting from scratch with no formal security program should budget toward the higher end.
The sticker price of an audit is only part of the story. A cheap audit from an inexperienced firm can leave you with a confusing report that enterprise customers will reject flat-out. That ends up costing you far more in lost deals and wasted time.
To really benchmark properly, get quotes from at least three firms and compare them on total scope, not just the headline number. We always recommend looking for auditors who offer fixed-fee pricing to protect yourself from surprise costs down the road.
For a personalized estimate based on your specific company profile, using an interactive tool like this audit cost calculator can give you a much clearer financial forecast.
Setting Realistic Audit Timelines
Just like with cost, the timeline for your SOC 2 depends on where you’re starting from. If your security controls and documentation are already in good shape, the process will be much quicker. If you’re starting from scratch, plan for a significant readiness phase.
A typical timeline has four stages:
- Readiness Assessment (1-6 months): This is where you, often with a consultant or the auditor, find and fix the gaps in your controls. How long this takes depends on your current security maturity.
- SOC 2 Type 1 Audit (1-3 months): This covers the fieldwork, where the auditor reviews your control designs, and the final report delivery.
- SOC 2 Type 2 Observation Period (3-12 months): This is the live monitoring window. Your controls have to be operating effectively throughout this entire time. A six-month period is a very common starting point for first-timers.
- SOC 2 Type 2 Fieldwork & Reporting (1-2 months): Once the observation period is over, the auditor comes back in to perform their testing and write up the final report.
All in, a first-time SOC 2 Type 2 can take anywhere from 5 to 20 months from the absolute start to the finished report. Plan for the full span if you need the report by a particular sales date.
The Main Categories of IT Audit Firms
IT audit companies aren’t interchangeable. They cluster into a few recognizable types, and the type a firm falls into gives a first read on cost, service style, and fit.
- Big Four (Deloitte, PwC, EY, KPMG): Global reach, integrated financial and risk services, and a brand that satisfies boards and public-company stakeholders. Best for large enterprises and complex multinational operations; usually overkill for a focused SOC 2.
- National and regional CPA firms: Established accounting practices with dedicated IT audit groups. Names that surface for “IT audit companies” include Cherry Bekaert, Baker Tilly, Wolf & Company, and similar firms. Strong for financial institutions and companies that want IT audit alongside their financial-statement work.
- Specialist / boutique security firms: Practices that do little except cybersecurity and compliance attestation. Current, active examples in the SOC 2 and broader IT audit space include Schellman, A-LIGN, KirkpatrickPrice, and Coalfire. Deep framework expertise, senior-led teams, and modern tooling.
- Automation-enabled auditors and platform partners: Firms that pair an audit practice with (or integrate tightly into) compliance-automation tooling so evidence can be pulled directly from your stack instead of collected by hand.
These categories overlap, and naming a firm here is descriptive, not an endorsement. Verify current accreditation and fit before you sign. To compare verified firms across cost, timeline, and framework coverage, start with our auditor directory.
Is a Big Four firm better than a specialist for a SOC 2 audit?
For a focused SOC 2 report, a specialist firm is usually the better fit for startups and mid-market SaaS companies. A Big Four firm fits large or public companies that also need financial-statement, tax, or risk work from one provider.
Choosing between a specialist, boutique IT audit company and one of the “Big Four” global accounting firms affects your budget, timeline, and the audit experience. (For a data-driven breakdown, see our deep dive on Big Four vs. specialist SOC 2 auditors.)
The right fit depends on your company’s stage, complexity, and goals. For most startups and mid-market SaaS companies, a boutique firm often delivers a more focused and responsive audit, particularly for frameworks like SOC 2 where specialist expertise matters.
The Case for Specialist Boutique Firms
Boutique firms specialize in frameworks like SOC 2, HIPAA, and ISO 27001. Their auditors are typically senior-level professionals who have spent their careers in information security and compliance.
That specialization usually means they know cloud environments, modern devops, and the security risks tech companies face.
Their smaller size usually translates to more direct access to experienced partners and a more agile, less bureaucratic process. You’re far less likely to get handed off to a junior associate who is learning on your dime. That usually means faster answers and more practical advice.
Key advantages often include:
- Deep Niche Expertise: They are masters of a few specific frameworks, not generalists trying to be everything to everyone.
- Greater Flexibility: Their processes can often be shaped around your company’s unique setup, not the other way around.
- Better Cost-Effectiveness: With lower overhead, their fixed-fee pricing is often more competitive.
- Senior-Level Attention: Your main contacts are seasoned auditors, not junior staff.
This flowchart shows how things like your company’s stage and complexity can influence what you should expect to invest in an audit.
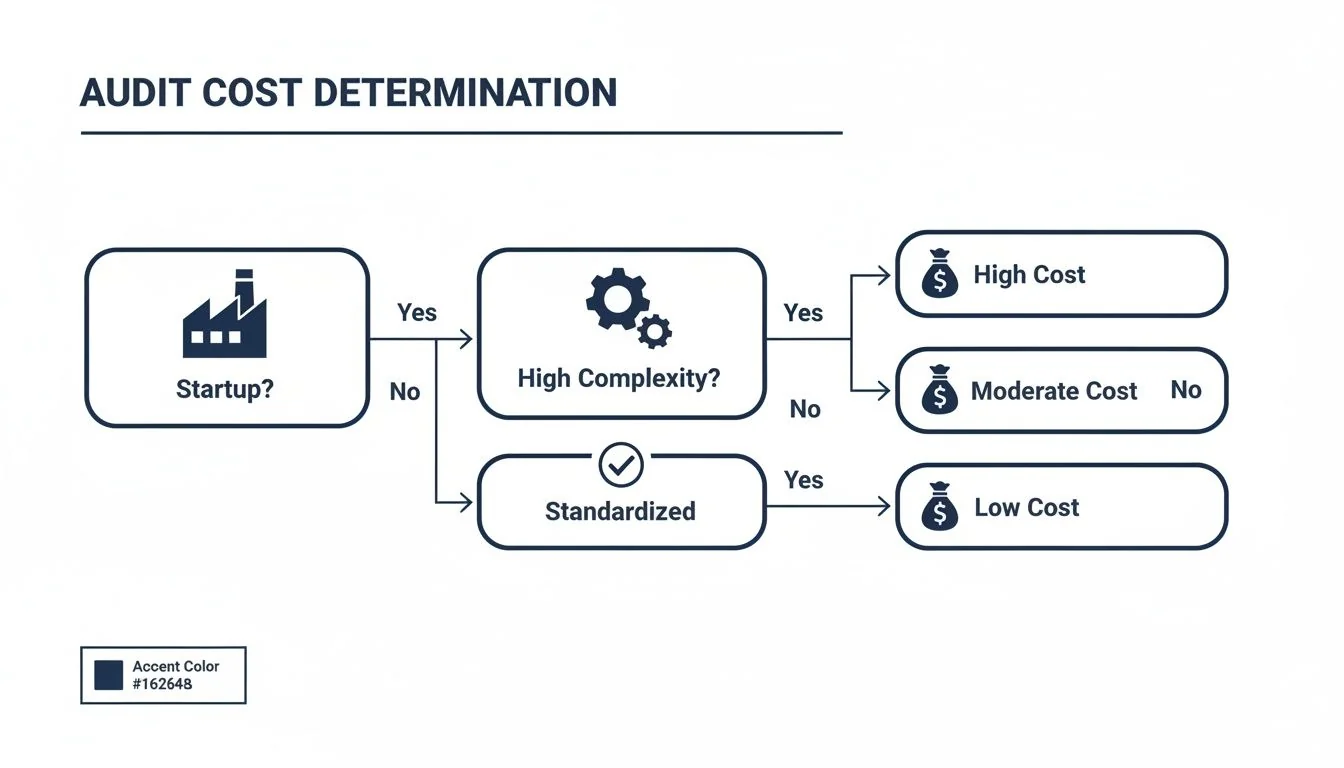
Startups with lower complexity often find much more cost-effective solutions with specialists. For larger, more complex enterprises, the costs tend to scale up regardless of the firm you choose.
When the Big Four Make Sense
The Big Four firms (Deloitte, PwC, Ernst & Young (EY), and KPMG) have global reach and a brand that boards and stakeholders recognize. For large, publicly traded enterprises or companies with complex international operations, that brand can provide the assurance stakeholders and boards demand.
Their primary strength is their ability to offer a huge, integrated suite of services that go way beyond a simple SOC 2 audit. If you need financial statement audits, tax advisory, and complex risk management consulting all under one roof, a Big Four firm is built for exactly that. Their global footprint is also a major plus for multinational corporations needing consistent audit services across different countries and regulatory landscapes.
For a Fortune 500 company, the integrated services and global brand recognition of a Big Four firm can matter. For a Series B SaaS company, that same structure can feel slow, impersonal, and too expensive for a focused SOC 2 audit.
But this scale comes with trade-offs. The teams assigned to smaller audit projects are often less experienced, and the rigid, standardized methodologies can feel clunky for agile tech companies. Costs are also significantly higher due to their massive overhead and brand premium.
Making the Right Choice for Your Business
Don’t choose an auditor based on brand recognition alone; pick the firm best equipped to handle your situation.
Comparison Specialist Boutique vs Big Four IT Auditors
This table compares the two on five attributes.
| Attribute | Specialist Boutique Firms | Big Four Firms |
|---|---|---|
| Ideal Client | Startups, mid-market tech, SaaS | Large enterprises, public companies |
| Core Strength | Deep SOC 2/ISO 27001 expertise | Broad service portfolio, global brand |
| Service Model | High-touch, partner-led | Formal, structured, often junior-led |
| Pricing | More competitive fixed fees | Premium pricing, higher overhead |
| Flexibility | Agile and adaptable processes | Rigid, standardized methodologies |
For most companies looking for a SOC 2 report to unblock sales deals, a specialist firm offers a more direct path to the report. Its focus, expertise, and service model fit the needs of a growing tech business better.
How do I choose an IT audit company?
Choose an IT audit company by matching its credential to the deliverable: a licensed CPA firm for SOC reports, an accredited certification body for ISO 27001, and a Qualified Security Assessor for PCI DSS. Then compare industry experience, the assigned team, report clarity, and fixed-fee pricing across at least three quotes.
Start by defining your audit scope. Before you even think about looking at IT audit companies, you need to know exactly what you’re auditing. Are you going for a SOC 2 Type 1 to check a box for a sales deal, or are you ready for the more rigorous Type 2? Which of the Trust Services Criteria (Security, Availability, Confidentiality, Processing Integrity, or Privacy) actually matter to the promises you’ve made to customers? Settling these answers makes your first calls with potential firms more productive.
Phase 1: Finding and Vetting Potential Firms
With your scope locked in, you can start building a list of reputable firms. Your goal is to create a longlist of five to seven potential partners. Instead of just Googling around, start with a curated list where you can filter by specialty and see verified metrics. Our auditor directory can serve as that starting list.
Once you have that longlist, whittle it down to three or four top contenders for initial discovery calls. In these meetings, your job is to cut through the sales pitch. You need to understand their methodology, the actual expertise of their team, and what the client experience is really like.
Here are the critical questions to ask on those first calls:
- What is your audit methodology? What specific tools do you use for evidence collection?
- Can you share an anonymized list of clients in our industry and of a similar size?
- Will we get a dedicated point of contact? What’s your guaranteed response time?
- Is your pricing a fixed fee? What are the most common reasons you issue change orders?
Phase 2: Analyzing Reports and Checking References
After the initial calls, ask your top two or three firms for a sanitized sample audit report. This is one of the best ways to judge the quality of their work. A good report is clear, professionally formatted, and easy for a non-technical person to read and understand. If the sample report is a confusing mess, that’s a red flag, and it will likely cause headaches for your own customers later.
Next, check their references. Don’t just settle for a list of their happiest clients. Ask to speak with a company that’s similar to yours in both size and industry. When you get them on the phone, ask specific questions about the audit process, how responsive the team was, and if they got hit with any unexpected costs or delays.
If a firm hesitates to provide relevant references or only offers generic contacts, consider it a warning sign.
Phase 3: Making the Final Decision
Finally, it’s time to review the proposals and pricing from your finalists. Don’t just look at the sticker price; focus on the total value. A slightly more expensive firm that offers a dedicated senior team, a modern audit platform, and a clear, fixed-fee structure is often a better investment than a cheaper option that leaves you with a confusing process and surprise bills.
Few companies hold formal assurance credentials. A Growth Market Reports analysis found that only about 18% of SaaS companies have a current SOC 2 report or ISO 27001 certificate. The gap is even wider for early-stage companies, where only ~7% of pre-seed and seed startups report SOC 2 compliance, compared to 45% of companies with over $100 million in funding.
Your Top Questions About Choosing an Auditor, Answered
These are the questions we hear most from founders, CISOs, and compliance leaders, from timing the search to switching firms.
When Should We Start Looking for an IT Audit Firm?
You should start your search three to six months before you want the audit observation period to kick off. Rushing the search is a mistake we see often, and it can lead to picking the wrong partner or missing deadlines.
That much lead time gives you a realistic window to properly vet a few firms, sit through scoping calls, negotiate the contract, and actually get on your chosen auditor’s calendar. More importantly, it builds in a buffer for readiness work. If a gap assessment uncovers serious gaps, you’ll have time to fix them without pushing back your target report date.
What’s the Difference Between a Readiness Assessment and an Audit?
A readiness assessment is a consultative project where a firm helps you find and fix control gaps before the formal audit begins. It’s collaborative and designed to get you ready.
The audit, on the other hand, is the official, independent examination by an accredited CPA firm. Its job is to give an impartial opinion on whether your security controls are designed correctly (Type 1) or actually working over time (Type 2). They’re two distinct things, but a good readiness assessment can make the audit go more smoothly.
Can We Switch Auditors Between a Type 1 and Type 2 Report?
Yes. Switching it audit companies between a Type 1 and Type 2 report is possible and common. Companies do it to find a better price for the more intensive Type 2, get better service, or find a firm with deeper expertise in their niche.
What matters is that there is no gap in your compliance coverage and that your control documentation and evidence pass cleanly from the Type 1 firm to the new firm.
What Red Flags Should We Watch Out for When Vetting Firms?
A few warning signs can tip you off to an inexperienced or non-transparent firm. Be wary if an auditor:
- Gives you fuzzy pricing: Vague estimates or a flat-out refusal to provide a fixed-fee quote is a recipe for surprise costs down the road.
- Can’t provide relevant references: If they can’t connect you with a client that looks like you (similar size, same industry), they probably don’t have the right experience.
- Uses high-pressure sales tactics: A real partner educates you and helps you make a good decision. They don’t try to rush you into signing a contract.
- Fails to explain their methodology: They should be able to clearly walk you through their process and explain what tools they use to make evidence collection less painful.
A refusal to share a sanitized sample report is one of the biggest red flags. That’s their final product, and if they won’t let you see the quality of their work, you should walk away.
What’s the Difference Between an IT Audit Company and a Cybersecurity Firm?
There’s heavy overlap, but the distinction is the deliverable. An IT audit company issues a formal, independent report or certificate against a defined standard, such as a SOC 2 attestation report, an ISO 27001 certificate, a PCI DSS assessment, or internal IT control testing. A pure cybersecurity firm typically focuses on technical testing and defense (penetration tests, threat detection, incident response) and may not hold the CPA license, QSA status, or accreditation needed to sign an attestation. Many specialists now do both, but if you need a signed report a customer will accept, confirm the firm carries the right credential.
Do All IT Audit Companies Cover SOC 2, ISO 27001, and PCI?
No. Coverage varies by accreditation. A CPA firm can sign SOC reports; ISO 27001 certificates come from accredited certification bodies; PCI DSS assessments require a Qualified Security Assessor. Some larger specialists hold all of these, but plenty of capable firms specialize in one or two. Always match the firm’s credentials to the specific deliverable you need rather than assuming one provider covers everything.
SOC2Auditors gives you verified data across our auditor directory, so you can compare real costs and timelines to find the right auditor for your business. Find your ideal auditor at https://soc2auditors.org.
More in Auditor Selection