 Menu
On this page
- Who does what in a Thoropass audit?
- What did Thoropass users report?
- How can a buyer prove the Thoropass workflow before signing?
- What can Thoropass Assurance decide, and what stays with the buyer?
- What do Thoropass reviews establish?
- What must the connected proposal include?
- When is Thoropass’s affiliated audit the right buy?
Thoropass belongs on the shortlist when you want compliance software, readiness help, and an affiliated audit path in one connected workflow. AWS Marketplace lists separate annual starting prices for the platform and SOC 2 audit; require both in your proposed order. Its audit-first path also merits a look if you want to keep your current GRC tool. Check your independence policy before adopting the bundle, and determine export and outside-auditor rights in writing if you may change CPA firms later.
Compare with: the Vanta review or the Drata review when choosing the CPA separately is a priority; Sprinto for guided preparation with a separately purchased audit.
Pros
- Connected platform and affiliated CPA audit path
- Audit-first path for teams keeping another GRC tool
- Expert guidance during readiness
- Evidence and auditor requests in one workspace
Cons
- Common ownership may conflict with buyer policy
- Outside-CPA access and export rights need written proof
- Published testing interval is unspecified
- Marketplace floors omit the complete engagement scope
Thoropass, formerly Laika, sells the software and services through Thoropass, Inc. Laika Compliance, LLC, doing business as Thoropass Assurance is the affiliated CPA firm. The buyer mistake is to treat its advertised import from another GRC tool as proof that any CPA can later work inside Thoropass. The Thoropass software profile holds the dated product record; our guide to the best SOC 2 compliance software by buyer fit explains the broader category.
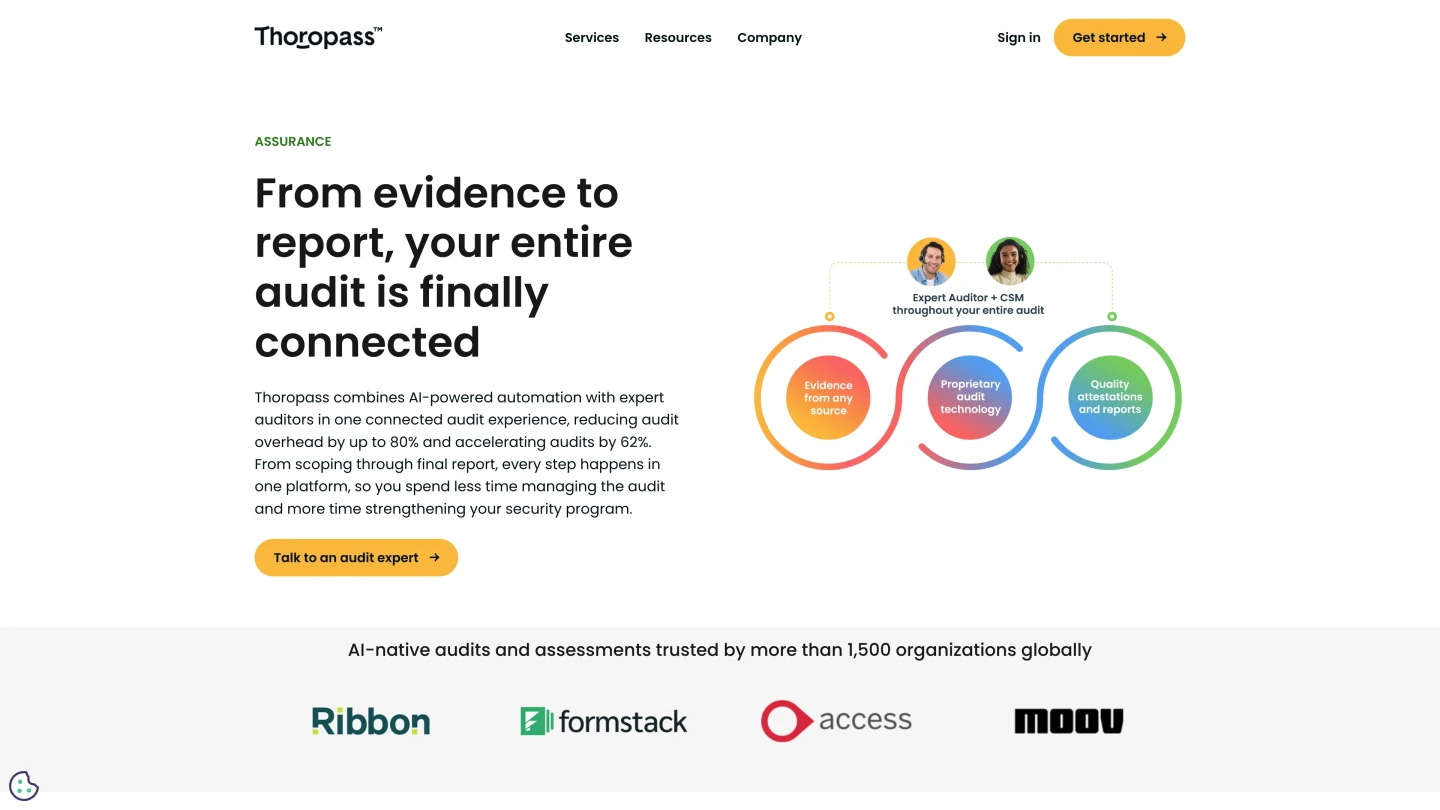
Thoropass’s public audit page presents the auditor and customer-success manager in one evidence-to-report path. The connection is the product claim to test, not a measured reduction in your own audit time.
Who does what in a Thoropass audit?
Thoropass describes a connected evidence-to-report workflow. The distinction buyers need is who provides each service, which direction evidence moves, and what the signed agreement permits.
| Part of the relationship | Publicly described path | Buyer proof |
|---|---|---|
| Platform and readiness | Thoropass, Inc. provides software and professional services, including customer-success guidance. The customer designs, operates, and remediates its controls. | Name the platform and service contracting entity, implementation work, evidence owners, and permissions in the order. |
| Examination | Affiliated Laika Compliance, LLC dba Thoropass Assurance performs the CPA audit. Thoropass says auditors see customer-selected evidence after submission. | Obtain the CPA engagement letter, report-signing name, independence assessment for the proposed engagement, and current peer-review record. |
| Keep another GRC tool | Thoropass says its audit-first path accepts exported files from another GRC tool; Smart Sort AI maps uploaded files to audit requests. | Upload a real export, inspect its source mapping with the audit team, and quote any platform access needed for that path. |
| Keep Thoropass, change CPA | The public material reviewed does not establish outside-CPA workspace access or a general right to rotate audit firms. | Get outside-CPA access, bulk export format, access window, transfer assistance, and fees written into the order. |
Sources: Thoropass's independence explanation and January 29, 2026 Smart Sort announcement, read September 25, 2026; Thoropass software profile. These vendor descriptions establish offered paths, not contractual portability, the independence conclusion for a particular engagement, or whether an uploaded item will satisfy the CPA.
Thoropass says its customer-success and audit teams are separate. The AICPA public peer-review file recorded a Pass for Laika Compliance, LLC, accepted December 12, 2025, for the period ending January 31, 2025. That firm-level result does not decide your engagement’s independence question. Thoropass itself cites an AICPA alert about potential self-review threats when a related CPA firm relies on a tool that becomes part of the customer’s controls. Have your CPA and procurement team assess the proposed use and your own policy; common ownership alone is neither a pass nor a failure for every buyer.
The direction matters. Thoropass’s Smart Sort announcement describes files coming into Thoropass from another GRC tool without an integration. It does not document a complete Thoropass record leaving for another CPA. Test each direction separately.
What looks useful, and where is the limit?
- One request path: Thoropass describes evidence collection, auditor collaboration, and report delivery in one workspace. Test whether the proposed audit team can trace an original artifact through a request and exception; the public page’s speed claims are vendor measurements.
- Keep the current GRC tool: The January 2026 Smart Sort announcement describes uploaded exports, not a live two-way sync. Ask the CPA to inspect missing metadata and incorrect mappings in a sample export.
- Account access: Thoropass documents SCIM setup for Entra and Okta. Its guide says SSO configuration and a requested API key come first, Google Workspace is unsupported for this path, and Okta catalog-installed apps do not currently work. Confirm the quoted edition and demonstrate provisioning and revocation rather than assuming every IdP path works.
- Exit and auditor choice: The public materials reviewed do not state outside-CPA workspace rights or a complete export entitlement. Treat both as contract questions, especially if annual auditor rotation is part of your policy.
What did Thoropass users report?
SOC2Auditors.org historical interviews with then-current Thoropass users, published September 11, 2026. Twenty-two role-labeled accounts, selected rather than representative; individual collection dates were not retained. Scores are self-reported, not a SOC2Auditors.org rating, and we do not average them.
Users who wanted a first SOC 2 without a GRC hire credited the people more than the software. A founder said Thoropass “basically gave us a compliance department before we could afford one,” and a security engineer called the people the differentiator. The lower scores came from teams further along. A vendor-risk manager, an enterprise security lead, and a GRC architect each scored it 3, and an admin who called the experience “much rougher than the reviews suggest” scored it 2.
The GRC architect raised the portability question this review asks: “I would personally prefer more separation and portability between compliance tooling and the audit engagement. I don’t want my GRC operating model shaped around one vendor.” That is one user’s preference, not evidence that Thoropass blocks an outside CPA. It is a reason to run the outside-CPA handoff test and get the export terms in writing.
| Buyer context | Interview evidence | What to prove before signing |
|---|---|---|
| First SOC 2 without a GRC hire | A founder and a security engineer credited the account team with making the first audit manageable; an operations manager became the internal compliance owner without a GRC background. A vCISO would put a first-time client on Thoropass but was “less convinced” for a sophisticated security organization. | Have the proposed customer-success contact work one ambiguous control with your owner; put the guidance scope in the order. |
| Audit-week coordination | A VP of legal said auditor requests and evidence in one environment replaced email chains. A GRC manager said readiness status meant jumping between roadmap items, tests, and requests. | Have the audit team request a sample, then show one view of everything still outstanding for the engagement. |
| Integration depth and test noise | A DevOps engineer said controls flagged items irrelevant to the environment and connectors needed reauthentication: “automation, not autopilot.” An IT manager uploaded more evidence manually than the demo suggested. | Connect your own sources, fail one test, and list every control that remains a manual upload. |
| Enterprise scope, vendor risk, or future auditor choice | An enterprise security lead found permissions and custom workflows strained; a vendor-risk manager called TPRM “a secondary module.” The GRC architect wanted tooling separated from the audit engagement. | Model your permissions and vendor list in the demo, then have a different CPA inspect a full export. |
Same interview scope as the interview note. Each row describes named respondents, not a measured segment average, and the interviews do not identify which respondents used Thoropass Assurance for the examination. The full role-labeled interviews appear below.
Read all 22 historical, selected user interviews; this is not a representative sample
| Role | What they said | Self-reported score |
|---|---|---|
| Founder | Thoropass basically gave us a compliance department before we could afford one. The biggest value wasn't the dashboard—it was somebody telling me what SOC 2 actually required and what to do next. We got through our first audit without hiring a GRC person. There are cheaper ways to do it, but I don't think they'd have been as painless. | 5 |
| CTO | The cloud integrations and automated evidence collection save us a meaningful amount of engineering time. AWS, GitHub, Google Workspace, HR systems—once they're connected, annual SOC 2 is much less painful. The UI isn't best-in-class and occasionally I still wonder where something lives, but overall it does the job extremely well. | 5 |
| Security Engineer | I've used several compliance platforms. Thoropass's differentiator is the people. When a control is ambiguous, I can get a useful answer instead of interpreting generic framework language myself. The product covers essentially everything we need for SOC 2, although Vanta/Drata sometimes feel more polished from a pure software perspective. | 5 |
| Compliance Project Manager | Framework mapping is one of the better parts of the product. Evidence can be reused across SOC 2, ISO and other programs rather than recreated from scratch. Support responds quickly and they've been shipping improvements. I'd like much more customization in the Trust Center and some additional certification support. | 5 |
| Compliance Director | We went from a very manual audit process to having evidence, controls and auditor communication in one place. That's a huge improvement. It saves us weeks around audit time. Whenever I've gotten stuck, the account team has been excellent. | 5 |
| VP Legal | Having the auditor and evidence requests in the same environment makes audits much faster. Instead of email chains and spreadsheets, I can see requests, upload evidence and have the conversation there. The vendor-management area feels less mature—the workflows are clunky and I'd love proper bulk editing. | 5 |
| Head of Engineering | Compliance is still work; Thoropass doesn't magically make SOC 2 disappear. But it turns a messy project into a fairly understandable set of tasks. Integrations eliminate a lot of screenshot gathering, and the support team is unusually pragmatic about how controls can actually work in an engineering organization. | 5 |
| CIO | Once the integrations and recurring reviews were configured, maintaining compliance became fairly routine. Monthly check-ins keep us honest. Custom reviews and some of the less-common workflows could be more flexible, but I'd buy it again. | 5 |
| Head of IT | It's particularly good at the boring operational stuff: policy acknowledgments, employee onboarding, evidence tracking, annual reviews and reminding people that tasks are overdue. My only complaint is that some workflows require more clicks than they should. | 5 |
| Cybersecurity Analyst | Being able to use the same evidence for multiple frameworks is a big efficiency gain. That's especially valuable when you're maintaining SOC 2 plus healthcare-related requirements. The human guidance has also been better than I expected from a software vendor. | 5 |
| Operations Manager | I was surprised by how quickly I could become the internal compliance owner without being a career GRC person. Delegating evidence requests is easy and reporting is much better than our spreadsheets. People/access management has some rough edges, custom integrations would help, and the questionnaire product isn't as strong as the core compliance workflow. | 4 |
| Engineering Director | Audit preparation is much smoother now and the integrations work well for our main systems. Where it loses a point is UX. The application has grown quickly and you can feel that—different modules don't always behave the same way and sometimes the obvious action isn't where I expect it to be. | 4 |
| DevOps Engineer | When an integration works, it's great: evidence just appears and I don't get dragged into audit week. But automated tests aren't infallible. We've had controls flag things that weren't actually relevant to our environment, and connectors occasionally need reauthentication. It's automation, not autopilot. | 4 |
| GRC Manager | The combination of software, audit coordination and experts is convenient. My frustration is that audit-readiness status could be more transparent. I sometimes have to jump between roadmap items, tests and evidence requests to figure out what is actually outstanding. | 4 |
| IT Manager | Good central system for controls, policies and evidence. New-user onboarding is easy enough. Some integrations aren't deep enough for our environment, so we're still manually uploading more evidence than the demo made me expect. Support usually helps us work around it. | 4 |
| Privacy Manager | The Trust Center makes customer diligence easier because Sales doesn't have to chase us every time somebody wants a SOC report or security document. I wish it had substantially more branding, permissions and workflow customization. As a trust portal it's useful, but not a product I'd buy by itself. | 4 |
| Security Analyst | Evidence collection and task ownership are good; notifications are less good. I'd like finer control over what gets emailed, when reminders go out and who gets them. Otherwise you eventually train yourself to ignore some of the noise. | 4 |
| vCISO | I'd happily put a first-time SOC 2 client on Thoropass because they'll get enough guidance to avoid common mistakes. For a sophisticated security organization with unusual controls and lots of custom workflows, I'm less convinced. The opinionated approach that helps beginners can become limiting later. | 4 |
| Vendor Risk Manager | Core compliance and audits are strong, but vendor risk feels like a secondary module rather than a full-strength TPRM product. Updating records and conducting reviews takes more manual effort than I'd expect. If vendor risk were my primary use case, I'd probably use something else. | 3 |
| Enterprise Security Lead | It works, but our organization has too many exceptions, business units and custom processes for the product to feel completely natural. The simpler your environment, the better the experience. Once you need complex permissions, customized workflows and enterprise reporting, the gaps become more noticeable. | 3 |
| GRC Architect | I like the convenience of the all-in-one model, but I would personally prefer more separation and portability between compliance tooling and the audit engagement. I don't want my GRC operating model shaped around one vendor. It's much more compelling for a company seeking its first few certifications than for a mature GRC organization. | 3 |
| Dissatisfied Admin | Our experience has been much rougher than the reviews suggest. Too many basic workflows feel unfinished, integrations produce noise, and fixes haven't always arrived quickly. The all-in-one idea was why we bought it, but we'd prioritize product maturity and flexibility much more heavily if selecting again. | 2 |
Same interview scope as the interview note.
How can a buyer prove the Thoropass workflow before signing?
Bring one control from your planned SOC 2 scope, an export from your current tool if relevant, and the proposed CPA engagement team. Ask for the action and retain the result:
- Control origin: Show the source system, collection permission, timestamp, mapped control, and original artifact. Keep both the source record and Thoropass view.
- Broken control: Make a test item fail or expire. Show alert timing, assigned owner, remediation, rerun, and preserved failure history. Thoropass markets continuous monitoring but publishes no uniform test interval; write down the interval for this control.
- Manual evidence: Upload a policy or approval record. Have an owner correct it, then show the old version, approval, and audit trail.
- Audit request: Have the intended Thoropass Assurance team request a sample, receive only the evidence the buyer submits, and record a question or exception. Keep the request and response history.
- Independence handoff: Ask which customer-success staff and auditors can see or change the same control record. Retain the permission demonstration and the engagement-specific independence documentation.
- Identity and role lifecycle: If SSO and SCIM are in the proposed edition, provision and revoke a buyer user through Entra or Okta. Then have Thoropass show customer-success and auditor access to the same control before and after evidence submission. Keep provisioning and revocation timestamps, role permissions, and the available access log or a written account of any missing log. Thoropass’s SCIM guide documents Entra and Okta setup but no public tier; confirm the quoted edition.
- Audit-first import: Export one control set from your current GRC tool. Upload it through the path Thoropass describes and have the CPA check source identity, dates, mapping, missing items, and correction history.
- Outside-CPA handoff: Export controls, mappings, artifacts, comments, requests, and version history from Thoropass. Ask a different CPA whether the files are usable without a Thoropass account. This is a proposed test, not a documented outside-CPA entitlement.
- Scope change: Add an entity, framework, or core system in a sample order. Record how readiness work, examination scope, access, and fees would change.
- Exit and renewal: Obtain the proposed export format, delivery time, post-termination access window, assistance fee, and audit-firm substitution term in the written order.
Run these proofs before signing. A successful screen share alone cannot establish access rights or an auditor’s conclusion about evidence sufficiency.
What can Thoropass Assurance decide, and what stays with the buyer?
Thoropass Assurance is the affiliated CPA firm that performs the examination and signs the report. The buyer owns control design, operation, remediation, policy approval, and the choice of evidence to submit. Thoropass says its auditors cannot see customer information until the customer submits selected evidence for review; confirm that boundary with the intended audit team in the actual workspace.
The CPA determines its procedures and evaluates exceptions. Thoropass software can collect, map, and share evidence; it cannot make a failed control pass. Ask the engagement team how it treats imported files, automated collections, and a control that changed during the observation period. The 2025 peer-review Pass is relevant firm-level context, not a substitute for those answers or for your procurement policy.
2 attestation-capable CPA firms in our auditor directory list Thoropass among the platforms they work with. That directory entry does not establish an official partnership, access to every Thoropass feature, or acceptance of a particular evidence set. If you are considering a different CPA, ask that firm to inspect the actual export and confirm its platform experience before you sign.
What do Thoropass reviews establish?
The G2 Thoropass product page is a software-review pool, not a score for Thoropass Assurance or each module. Our software record captured 4.7/5 across 582 G2 reviews on September 11, 2026. G2 did not expose a readable current aggregate during the September 28 check, so that figure remains a dated snapshot, not a fresh rating or our own product score. It is a separate population from the selected interviews above. Search results also surface Thoropass Glassdoor employer reviews; those assess employment, not the compliance product.
Public discussion adds two narrow checks. A September 2025 r/sysadmin poster said Thoropass had not made the audit process more efficient for an Azure and on-premises environment and questioned the price. A July 2026 r/soc2 commenter reported that Thoropass helped through a difficult first SOC 2 process, while still calling it expensive. These are self-selected accounts with different scopes; neither establishes a typical customer outcome. They make an environment-specific evidence demo and a complete quote more useful than an average star rating.
What must the connected proposal include?
The Thoropass proposal should identify software, readiness work, the CPA examination, implementation, support, additional frameworks, renewal, and exit terms as separate lines. On September 11, 2026, AWS Marketplace listed starting annual dimensions of $8,700 for the platform and $5,800 for a SOC 2 audit. They bill independently on that listing and are listing floors, not an all-in quote for your scope. The Thoropass pricing guide keeps the dated commercial detail.
Name Thoropass, Inc. and Laika Compliance, LLC where each is the contracting party. Ask what the audit-first order costs if you keep another GRC platform, and what changes if you later use another CPA. Include security work, internal owner time, and any separately purchased audit fee when comparing an unbundled proposal.
When is Thoropass’s affiliated audit the right buy?
Shortlist Thoropass when the proof steps show a usable control-to-CPA path and the proposed relationship fits your governance rules.
| Buying situation | Shortlist direction | Reason to test |
|---|---|---|
| Want software, readiness guidance, and an affiliated CPA audit in one workflow | Thoropass connected offer | The shared request path may reduce handoffs; buyer-owned controls and the engagement-specific independence assessment still matter. |
| Like the current GRC tool but want Thoropass Assurance for the audit | Thoropass audit-first offer | The vendor advertises an import path. Prove mapping, exceptions, CPA review, and the exact access charge. |
| Require a CPA firm with no common ownership with the software provider | Vanta or Drata with a separately selected CPA | That buyer policy may exclude the affiliated path regardless of the firm's peer-review result. |
Compare Thoropass vs Vanta for the connected audit and Seamless Audit paths, or Thoropass vs Drata for auditor choice and multi-framework scope. Neither comparison establishes audit quality or a right to substitute firms; check the proposed order and CPA engagement letter.
The decision file should contain a sample failed-control record, an auditor request and response, a usable export checked by the intended CPA, and the two entities’ written scope. One question remains open in public materials: can an outside CPA inspect and work in the Thoropass workspace on the same terms as Thoropass Assurance? Get that answer in the order if future auditor choice is part of your buying case. Software-only alternatives to the connected path are in the SOC 2 software directory.
More in Compliance Tools