 Menu
On this page
- Scytale Pros and Cons for a SOC 2 Program
- What You Actually Buy: Platform Only, or Software Plus a Named Expert
- Does Scytale Fit Your Stack?
- What Scytale Automates vs What Your Team Still Owns
- How Scytale Works With Your CPA
- What Does Scytale Cost?
- What Real Scytale Reviews Say
- Scytale vs Vanta for SOC 2
- Is Scytale Worth It? How to Decide
- Frequently Asked Questions About Scytale
- Final Verdict and Next Steps
- How We Researched This Review
Our verdict: Scytale is a strong shortlist candidate for a first SOC 2 or ISO 27001 when the team will actually use the dedicated GRC expert, and when cloud, source-control, and identity systems look like the ones Scytale already tests. It is weaker when you need a number on the marketing site, when the stack is unusual, or when you expect the platform to replace remediation and the CPA audit.
Who this is for: Founders, engineering, and operations leaders deciding whether Scytale fits a SOC 2 program. Employer reviews of working at Scytale are a different search.
Best alternatives: Vanta for a broader connector catalog and a much larger G2 sample, Drata for Audit Hub review volume, and Comp AI for inspectable or self-hosted code. Prices and quote inputs are in the Scytale pricing guide.
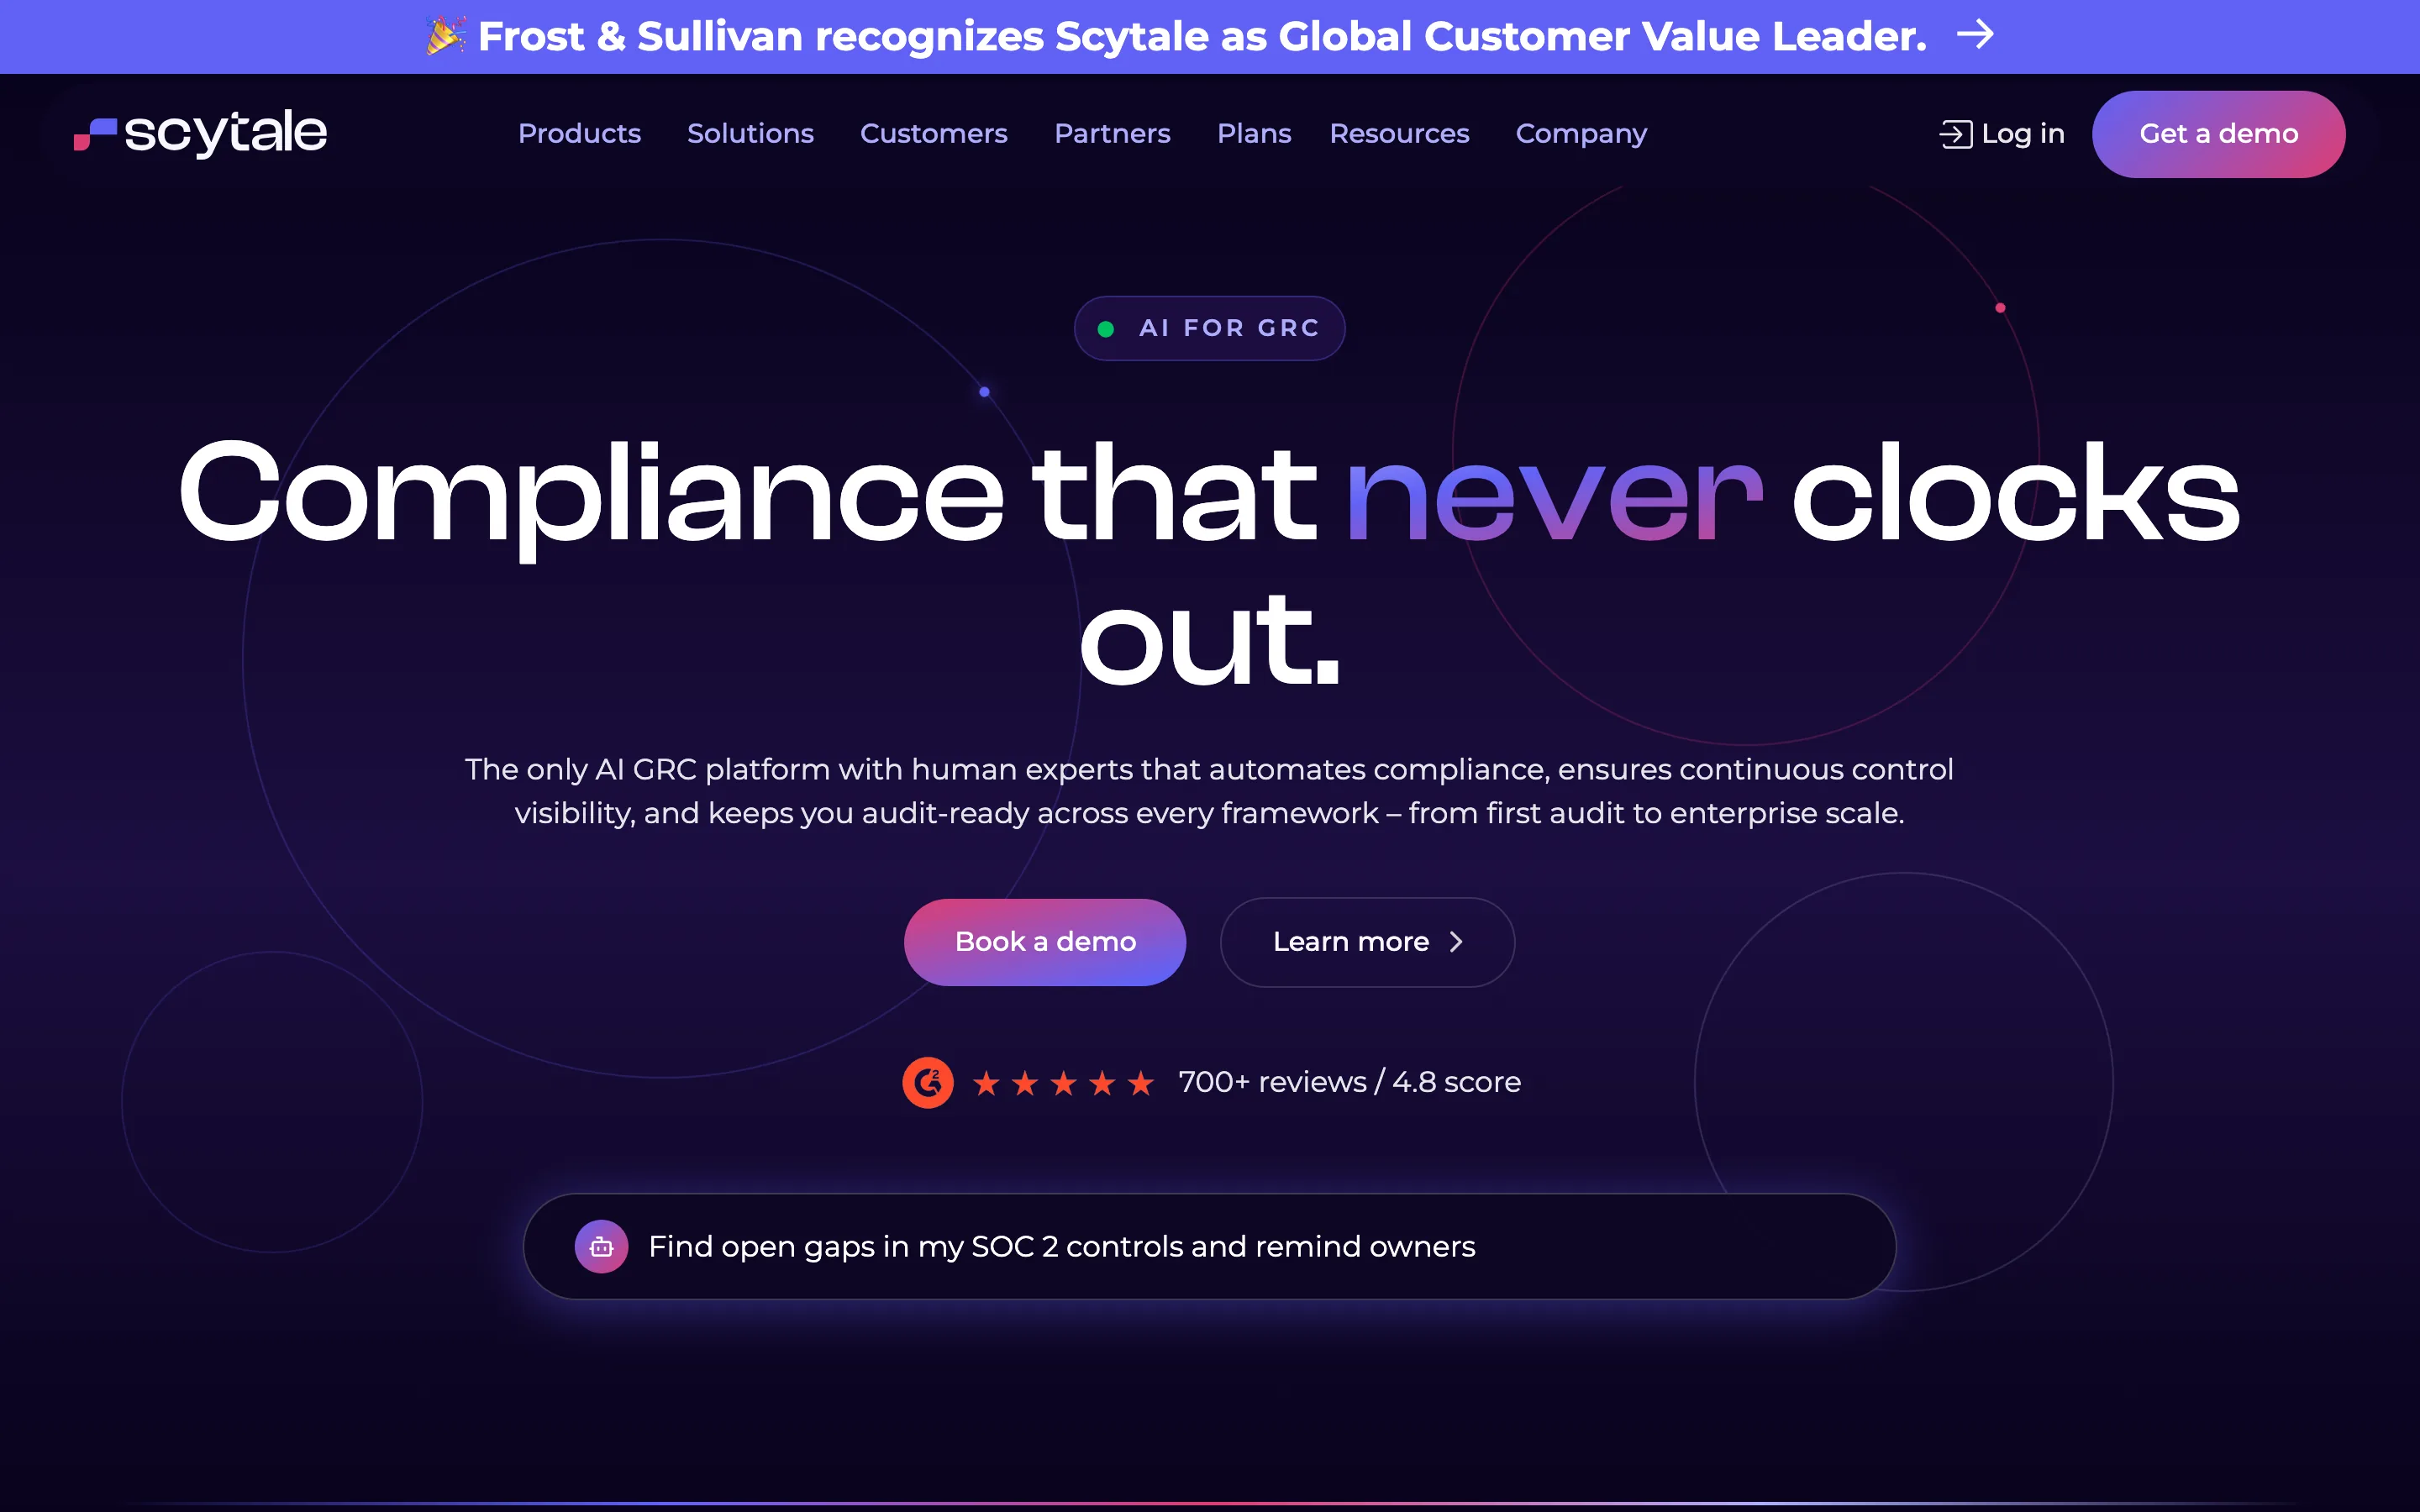
Scytale is a SOC 2 and multi-framework compliance platform that sells software and, in most startup packages, a named GRC expert in the same buying path. Decide first whether you are buying the expert, then whether your stack matches the connectors. We used the product and interviewed 21 current users. G2 showed 4.8/5 across 734 reviews on September 11, 2026. AWS Marketplace still listed the platform plus one framework from $7,500 for 12 months.
For quote inputs and the AWS starting prices, use the Scytale pricing guide.
Scytale Pros and Cons for a SOC 2 Program
Scytale centralizes policies, controls, and evidence, and the consulting bundles put a person on the account who already knows what an auditor will ask for. Your team still remediates failures, and an independent CPA still performs the examination.
Key Strengths (Pros)
- Dedicated GRC expert: Build DFY includes a consultant for up to six months; Build Stronger includes one for 12 months. A fractional GRC lead we interviewed called that person the differentiator: plenty of products collect AWS or GitHub evidence; Scytale gives you someone who translates what the auditor wants into work for the team. Build Starter does not include that consultant.
- Control-mapped evidence: An IT manager said the biggest win was everything tying back to specific controls instead of screenshots living in five departments. A software engineer said AWS and GitHub integrations replaced proving the same things every cycle, and that engineers could see what they owned.
- Auditor hub: Scytale’s pricing matrix lists an auditor hub as a base feature. We used the product as a shared evidence workspace. We did not independently test every auditor permission or every export path. Invite the intended CPA to inspect a representative package before you sign.
- Cross-framework mapping: A GRC manager used Scytale as a single control-and-evidence repository so a second certification did not start from a blank folder. Scytale reports 80+ frameworks; that total includes smaller, divisional, and add-on frameworks. Our directory has eight sourced pages: SOC 2, ISO 27001, ISO 42001, HIPAA, PCI DSS, GDPR, SOX ITGC, and C5.
Key Limitations (Cons)
- Quote-only pricing: scytale.ai/pricing still shows no dollar rates. The public number is the AWS Marketplace floor, not a complete invoice.
- Stack-dependent automation: A DevOps engineer scored 4 after automated checks misread a setup that was actually fine. An IT security manager still wanted more integrations and fewer manual-evidence gaps. Catalog presence is not evidence depth.
- Platform still maturing: A regulated-startup founder scored 4 after integrations failed to populate and policies or training syncing broke. Support fixed the incidents. The founder still described the product as maturing. G2’s cons tags on September 11, 2026 still included Integration Issues (43) and Limited Integrations (32).
- Separate audit fees: Scytale is not the licensed CPA firm that issues the SOC 2 report. AWS Marketplace lists a third-party audit service from $4,200 as a starting dimension. Confirm the firm’s identity, independence, scope, and complete fee.
Scytale at a Glance
- Category and origin: SOC 2 / multi-framework compliance automation platform. Founded 2021 by Meiran Galis. Closed SaaS; the AI GRC agent is named Scy.
- Integrations and testing: 150+ confirmed by Scytale’s marketing team on August 11, 2026. G2’s product page listed 99 integrations on September 11, 2026; those are different counts. Testing is vendor-claimed 24/7 continuous monitoring; the interval is unpublished. We did not measure that interval.
- Dated G2 aggregate: 4.8/5 from 734 reviews on September 11, 2026. Homepage marketing displayed 700+ / 4.8 the same day. AWS Marketplace showed 4.8 across 731 ratings, a lagging count.
- Plans and spend: Build Starter is platform-only. Build DFY bundles LaunchReady consulting and a black-box web-app pen test. Build Stronger bundles StayReady consulting and a gray-box web-app pen test. AWS Marketplace listed the platform plus one framework from $7,500 for 12 months on September 11, 2026. The upper bound is unknown.
- Audit and timing: The subscription does not include a CPA opinion. Scytale’s own guidance says most companies reach SOC 2 audit-readiness in 3 to 12 months. A Type II observation window is set with the CPA; the consultant cannot shrink it.
What You Actually Buy: Platform Only, or Software Plus a Named Expert
Scytale sells a platform-only starter package and two startup bundles that include a dedicated consultant. Those are not the same product. The homepage line about being the only AI GRC platform with human experts describes the consulting bundles, not Build Starter.
The public pricing page, captured September 11, 2026, still names Build Starter, Build DFY (Done for you), and Build Stronger. It still shows no dollars.
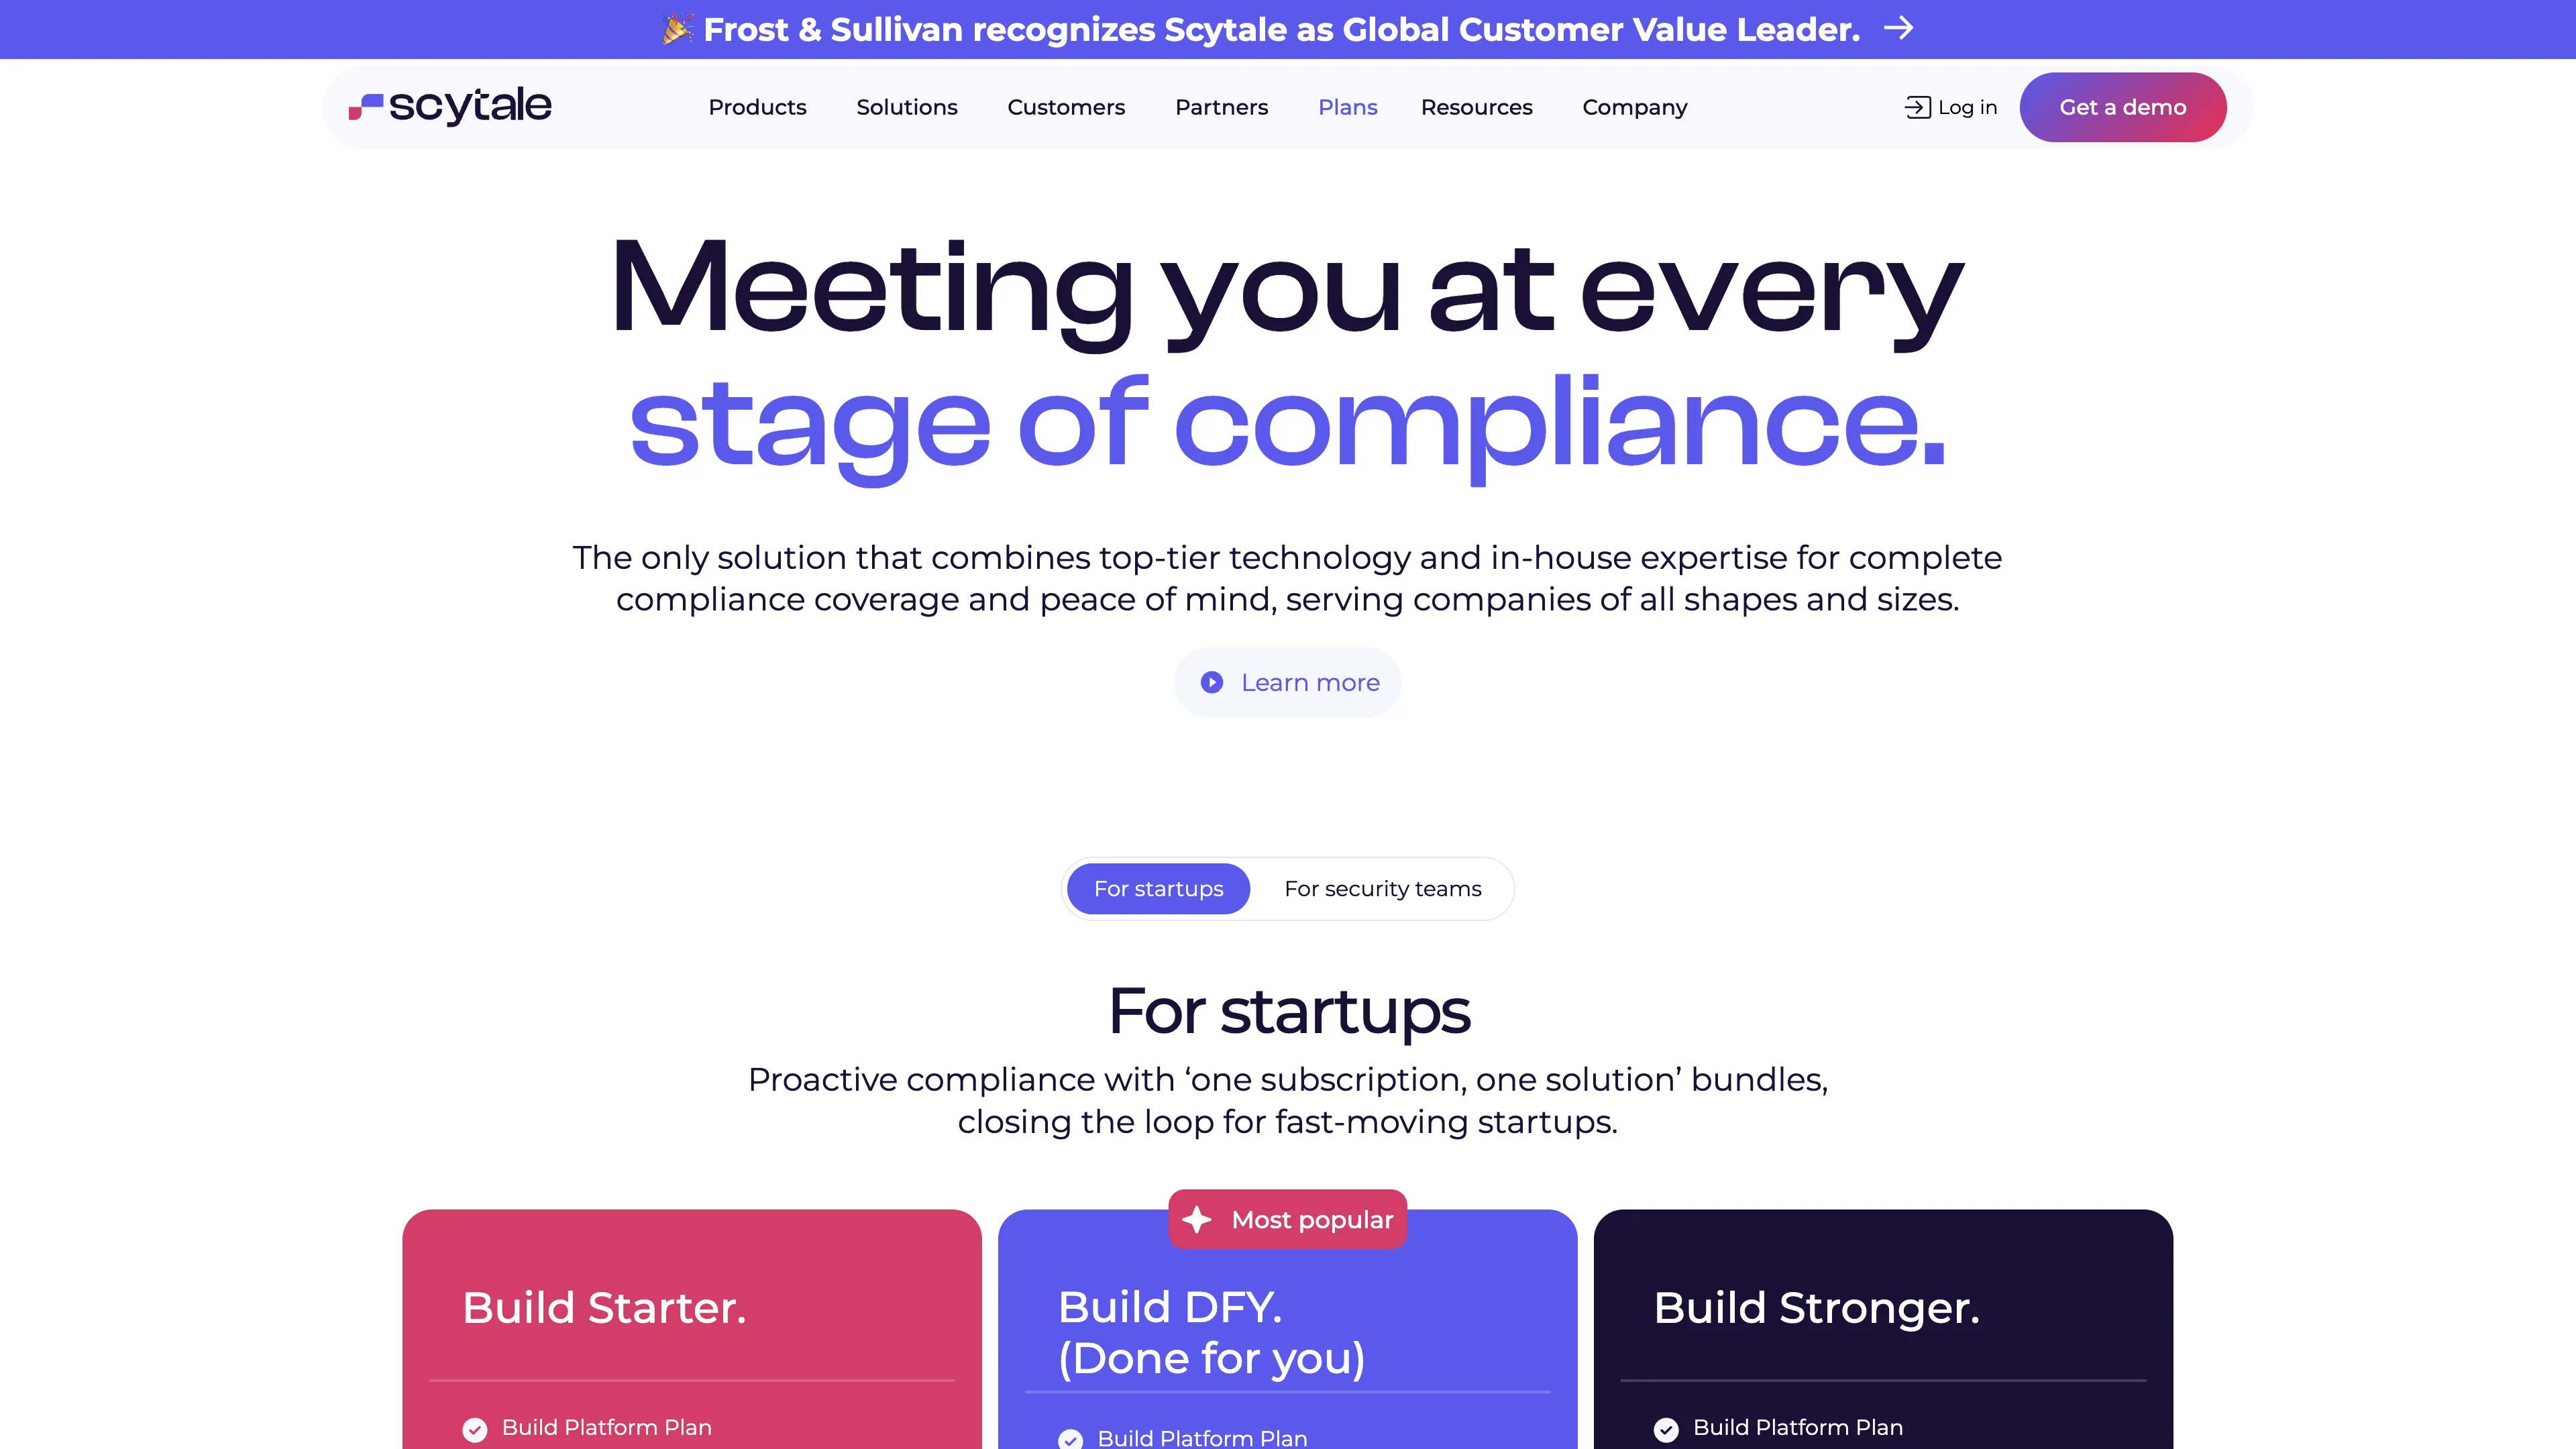
Build DFY includes LaunchReady: a dedicated consultant for a maximum of six months, weekly project calls until audit completion, one-time policy alignment, and a black-box web-app penetration test. Build Stronger includes StayReady: a dedicated consultant for 12 months, ongoing policy updates, regular calls based on audit proximity, and a gray-box web-app penetration test. Both list one framework, with add-ons available. ComplianceShield is a separate dedicated GRC-team / vCISO offer, not the default startup buy.
| Buying input | Build Starter | Build DFY (LaunchReady) | Build Stronger (StayReady) |
|---|---|---|---|
| Dedicated consultant | None listed | Named GRC expert, maximum six months | Named GRC expert, 12 months |
| Call cadence | Platform-led | Weekly project calls until the audit | Regular calls based on audit proximity |
| Policy work | Platform templates | One-time policy alignment | Ongoing policy updates |
| Pen test in the bundle | Not in this package | Black-box web app | Gray-box web app |
| Frameworks | One; add-ons available | One; add-ons available | One; add-ons available |
| Who this is for | A team that already has a compliance owner and wants software only | A first SOC 2 without a GRC hire, through audit | A first year plus staying compliant after the report |
Sources: Scytale pricing page, retrieved August 31 and September 11, 2026, via the Scytale software record. Put the named expert, included hours, channel, and what happens after the audit in the Order Form. ComplianceShield is a separate dedicated GRC-team offer.
A 10–30 person SaaS founder we interviewed compared Scytale with Vanta and Drata and paid for the walkthrough, not another dashboard. Ask for Starter and DFY as separate line items. A quote that calls both “Scytale” hides whether you are paying for the consultant.
Does Scytale Fit Your Stack?
Interview scores stayed at 4 or 5 even when automation misfired, because the consultant was part of the product. The three 4s were false positives, sync bugs, and a confusing start. We do not average those scores into a Scytale rating. They are the interviewee’s, not ours.
| Environment | What users reported | Self-reported scores in this set | Decision check |
|---|---|---|---|
| Standard cloud / SaaS (AWS, GitHub, common identity and HR tools) | Integrations saved engineers from proving the same things every cycle. Tasks arrived with context instead of a vague “prove 100 things.” | Mostly 5 | Give Scytale your actual inventory and collect one representative control from each critical system in a demo. |
| Unusual or custom infrastructure | Checks can misread a setup that is actually fine, or flip a control to failing. Manual evidence remains where connectors do not cover the environment. | 4 from a DevOps engineer and a regulated founder | Ask for exclusions, configuration, and a written list of what stays manual. Do not buy from the 150+ catalog claim. |
| First-time team, no GRC hire | The expert is the buy reason. The dashboard becomes the system of record. Coordination overhead drops more than any single automation feature. | 5 | Put the named expert, hours, and what happens after the audit in the order form. Build Starter is the wrong SKU for this case. |
| After kickoff / program manager | Dashboards and structure worked once scope, phases, and ownership were aligned. The start was the friction. | 4 from a compliance program manager | Insist on a scoping session before you treat the workflow as self-explanatory. |
SOC2Auditors.org interviews with 21 current Scytale users, plus Scytale's vendor-confirmed 150+ integrations (2026-08-11). Scores are self-reported; we do not average them.
A failed sync still returns you to troubleshooting or a manual upload. For an unusual environment, run a proof of concept against the systems you cannot replace.
What Scytale Automates vs What Your Team Still Owns
Scytale collects connected evidence, maps it to controls, and tracks remaining work. Engineers still fix failing checks in the source system. The GRC expert coaches exceptions. Scytale does not issue the SOC 2 opinion.
The pricing matrix lists 24/7 continuous monitoring and on-demand checks. The testing interval is unpublished. We used the product; we did not independently measure every connector or every check’s runtime. Treat homepage “24/7” as marketing until Scytale shows the interval on your stack.
- 01DetectAn automated check or a consultant review flags a control, missing evidence, or an exception.
- 02Assign ownerRoute a discrete task to the engineer, HR owner, or department lead who owns the source system.
- 03Fix in source systemChange the configuration, policy, or process. Do not treat a green or red badge as the fix.
- 04Rerun or uploadRe-collect evidence, wait for the next check, or upload manual proof where the connector does not cover the setup.
- 05Evidence / resultKeep the timestamped result in the auditor hub for the CPA.
What Scytale Automates
- Evidence ingestion: Connected integrations query cloud, source control, identity, and other systems. A software engineer said that is the part that stays out of engineering’s way. A security engineer still would not blindly trust every green or red status.
- Task and policy workflow: Assignments, training, people evidence, and recommended actions turn a framework into work. An HR manager who is not a security specialist could still see what Scytale needed. An engineering manager wanted better bulk actions and notifications.
- Access reviews: A head of engineering used user-access reviews so engineering got discrete tasks rather than a periodic dump of 100 proof requests. Scytale’s pricing matrix lists automatic access reviews. We did not independently measure them at 1,000-employee scale.
- Trust center and questionnaires: Scytale documents a trust center and AI questionnaire answering via Scy. Some Scy functions are limited by tier. We did not independently measure pre-fill rates.
What Your Team Still Owns
- Technical remediation: A failing check names a control. Engineers still change AWS, GitHub, or the identity provider.
- Exceptions the connector cannot see: An IT manager still had manual evidence where integrations did not cover the environment.
- Written vs practiced policy: Templates and one-time alignment are a draft. Auditors test whether people follow the written procedure.
- Internal governance: A GRC manager said the tool removes administrative work. It does not remove the need for good internal governance.
- CPA coordination: The auditor hub shares evidence. The firm still samples, tests, and signs.
A compliance program manager said the start was the hard part: scope, phases, and ownership were not obvious until the Scytale manager aligned them. After that, the dashboards worked.
How Scytale Works With Your CPA
Scytale gives your company, the GRC expert, and an invited CPA a shared evidence workflow. It does not conduct the examination or issue a SOC 2 opinion.
Some packages include auditor coordination. AWS Marketplace lists a third-party audit service from $4,200 as a separate starting dimension. That line does not name the licensed firm, prove independence, or cap the examination fee. Confirm the CPA in writing before you treat a Scytale quote as all-in.
| Owner | What they control | What moves through Scytale | What still needs judgment |
|---|---|---|---|
| Your company | Scope, control design, remediation, evidence quality, audit period, and which firm is invited. | Mapped evidence, task status, policies, and export packages. | Whether controls describe reality and exceptions are closed. |
| Scytale software | Collection workflows, automated checks, mappings, auditor hub, and role permissions. | A shared view of controls, evidence, and progress. | Whether an automated result is enough evidence for the auditor's procedure. |
| Scytale GRC expert | Scoping, what the auditor actually wants, exception coaching, and keeping the team moving. Duration depends on LaunchReady vs StayReady vs Starter. | Answers what to do next. Does not change source-system configuration or sign the report. | Whether the advice matches how the company actually operates. |
| Independent CPA | Sampling, testing, follow-up requests, exceptions, and the final SOC 2 opinion. | Review of the invited workspace and any package the firm accepts. | Nature, timing, and extent of testing — and whether the evidence supports the opinion. |
Source: Scytale pricing and SOC 2 product pages, retrieved via the Scytale software record; CPA responsibility is SOC2Auditors.org's editorial clarification. Scytale does not issue the SOC 2 report.
Browse an independent shortlist in our auditor directory before you treat a referred fee as the market.
What Does Scytale Cost?
Scytale does not publish dollar rates on its own site. The public number is the AWS Marketplace floor, and every other line on that listing is still a quote.
On September 11, 2026, the AWS Marketplace seller listing still showed the platform plus one framework from $7,500 for 12 months. That is a public starting floor, not a complete quote. The upper bound remains unknown.
Extra frameworks, consulting, penetration testing, virtual compliance, questionnaires, and third-party audit services appear as separate starting dimensions on that listing. Do not add them up and call the sum a Scytale price. The Scytale pricing guide has the dated table and the quote-normalization checklist.
Budget the platform, the expert hours you actually need, and the CPA examination separately. Use the SOC 2 audit cost guide for the examination.
Questions to resolve before you sign
- Which package is in the quote: Build Starter, Build DFY / LaunchReady, Build Stronger / StayReady, or ComplianceShield?
- Who is the named expert, for how many months, and what happens to that channel after the audit?
- Which connectors and framework maps were demonstrated on your stack?
- Which checks stay manual, and can you exclude or reconfigure a false fail?
- Which licensed CPA firm, deliverables, and fee are included or excluded?
- What bulk-export rights exist if the CPA wants an offline folder?
- What is the initial term, renewal notice date, and data-return process?
What Real Scytale Reviews Say
G2 is the dated public rating: 4.8/5 from 734 reviews on September 11, 2026. The interviews below are ours. Reddit posts are separate public reports. Glassdoor results for “scytale review” are employer reviews, not this product.
Interviews with current Scytale users
We interviewed 21 current users, from founder and CTO to CISO, HR manager, DevOps engineer, and a regulated-startup founder. They are not a random sample. More interviews are in progress. We do not average their self-reported scores into a Scytale rating.
Small teams used it so a founder would not have to become the compliance expert. Engineers wanted discrete tasks and connectors that stay out of the way. The 4s wanted exclusions for unusual infrastructure, fewer sync bugs, and a clearer start.
- Founder / CTO: “We needed SOC 2 quickly without hiring a compliance person. Scytale basically told us what controls mattered, what evidence was missing, and what to do next. The dashboard and automated evidence took a lot of the chaos out of it. The real value was having a human expert keeping us moving.”
- Fractional GRC Lead: “The dedicated GRC person is the differentiator. Plenty of products can collect AWS or GitHub evidence; Scytale gives you someone who understands what the auditor actually wants and translates that into work for the team. That cuts a lot of pointless back-and-forth.”
- SaaS Founder: “I compared this category with the likes of Vanta and Drata. Scytale’s appeal is that I’m not buying a dashboard and then becoming the compliance expert myself. For a small company, having someone walk us through the audit and keep us accountable is the thing I’d pay for again.”
- DevOps Engineer: “Automation is useful when your infrastructure looks the way Scytale expects. When it doesn’t, evidence checks can misread something or flip a control into a failing state even though the underlying setup is fine. I want more exclusions, configuration and transparency around automated tests.”
All 21 interview quotes
| Role | What they said | Self-reported score |
|---|---|---|
| Founder / CTO | We needed SOC 2 quickly without hiring a compliance person. Scytale basically told us what controls mattered, what evidence was missing, and what to do next. The dashboard and automated evidence took a lot of the chaos out of it. The real value was having a human expert keeping us moving. | 5 |
| Early-stage CEO | Compliance went from this scary side project that could swallow months of management time into something structured and predictable. I can actually see where we stand. It’s expensive compared with doing everything yourself, but much cheaper than distracting half the company. | 5 |
| IT Manager | Everything being tied back to specific controls is the biggest win. I’m no longer chasing screenshots and spreadsheets across five departments. There’s still some manual evidence where integrations don’t quite cover our environment, but audit prep is substantially easier. | 5 |
| Head of InfoSec | For ISO 27001, I like having policies, risks, controls, evidence and audit readiness in one place. It gives management a much clearer picture. I’d like deeper configuration in some areas, but it has become our compliance system of record. | 5 |
| Fractional GRC Lead | The dedicated GRC person is the differentiator. Plenty of products can collect AWS or GitHub evidence; Scytale gives you someone who understands what the auditor actually wants and translates that into work for the team. That cuts a lot of pointless back-and-forth. | 5 |
| SaaS COO | It lets a small team run SOC 2 or ISO without building a compliance department. Assignments, policies, evidence and progress are centralized. From an operations perspective, the reduction in coordination overhead is probably more valuable than any single automation feature. | 5 |
| Software Engineer | The AWS/GitHub integrations save me from manually proving the same things every audit cycle. Engineers can see exactly what they’re responsible for instead of getting vague compliance requests. It stays mostly out of our way, which is what I want from compliance software. | 5 |
| DevOps Engineer | Automation is useful when your infrastructure looks the way Scytale expects. When it doesn’t, evidence checks can misread something or flip a control into a failing state even though the underlying setup is fine. I want more exclusions, configuration and transparency around automated tests. | 4 |
| CISO | The roadmap to certification is very clear. Controls are mapped, progress is visible, and the consultant helps us work through exceptions instead of just flagging them. It’s particularly good if your security team is small. | 5 |
| HR Manager | I’m not a security specialist, and I can still understand what Scytale needs from HR. Training, policies, people evidence and assigned tasks are straightforward. Occasionally the workflow feels more rigid than our internal processes, but the guidance makes up for it. | 5 |
| Operations Manager | Before this, compliance was Slack messages, spreadsheets and folders everywhere. Now everyone can see the outstanding tasks and evidence. The biggest improvement is knowing what ‘done’ actually means instead of constantly wondering whether we’ve missed something. | 5 |
| Founder (regulated) | The weekly consultant touchpoints were excellent. The software was generally easy, but we ran into integrations not populating properly and some syncing bugs around policies or training. Support fixed things, but the platform itself still feels like it is maturing. | 4 |
| Compliance Program Manager | Once we got moving, the dashboards and structure worked well. My frustration was the beginning: scope, phases and ownership weren’t immediately obvious, and some workflows could be more flexible. After aligning with the Scytale manager, things became much smoother. | 4 |
| Privacy Operations Manager | It turns compliance requirements into actionable work instead of leaving me to interpret a framework from scratch. Having documentation, recommended actions and a person to ask makes a huge difference. I’d especially recommend it to businesses without a large internal GRC function. | 5 |
| Head of Engineering | Integrations with cloud, source control and other systems eliminate a lot of evidence gathering. User-access reviews are useful too. It means engineering gets discrete tasks rather than somebody periodically asking us to prove 100 things at once. | 5 |
| IT Security Manager | The evidence collection is genuinely useful, and having security/GRC expertise available means I’m not alone interpreting every requirement. My wish list is more integrations, better automation for unusual environments and fewer places where we have to fall back to manual evidence. | 5 |
| GRC Manager | Scytale gives me a single control-and-evidence repository across frameworks. The cross-mapping matters because we’re not starting over every time we add another certification. The tool doesn’t remove the need for good internal governance, but it removes a lot of administrative work. | 5 |
| Finance / Ops Lead | The benefit I notice is commercial. Certification stops being this indefinite project holding up customer conversations. We know what is outstanding and can get through the process faster, which helps with enterprise procurement and due diligence. | 5 |
| Security Engineer | I like the continuous evidence idea much more than taking screenshots once a year. Some automated checks still need human judgment, so I wouldn’t blindly trust every green or red status. But as the place where evidence and controls live, it works well. | 5 |
| Engineering Manager | It’s easy enough that non-compliance people can participate. I can assign a task to an engineer or department owner and give them context. I’d still like better bulk actions, notifications and workflow-management features so there’s less clicking around. | 5 |
| SaaS Founder | I compared this category with the likes of Vanta and Drata. Scytale’s appeal is that I’m not buying a dashboard and then becoming the compliance expert myself. For a small company, having someone walk us through the audit and keep us accountable is the thing I’d pay for again. | 5 |
SOC2Auditors.org interviews with current Scytale users. Roles only; no company names. Self-reported scores are the interviewee's, not a SOC2Auditors.org rating. More interviews are in progress.
G2 Aggregate
On G2, Scytale held 4.8 out of 5 stars across 734 reviews on September 11, 2026. Scytale’s homepage showed 700+ reviews / 4.8 the same day; we use the public G2 product page, not the marketing badge. AWS Marketplace showed 4.8 across 731 ratings. We did not code a representative G2 sample, so the star average does not say how common any single praise or complaint is.
The dated star split on that G2 page was 648 five-star, 83 four-star, 2 three-star, 0 two-star, and 1 one-star.
G2 also publishes all-segment “value at a glance” fields (time to implement, time to ROI). Those are G2’s fields, not a measurement from our tenant or interviews.
Practitioner Reports From Reddit and HackerNoon
These are individual posts, not a sample:
- Smooth Scytale path: In r/SaaS, one commenter wrote that they went with Scytale and ConstellationGRC, that integrations and evidence were easy, and that support was smooth.
- Vanta cheaper overall: Another commenter in that thread said Vanta ended up cheaper. That is one person’s spend note, not Scytale’s rate card and not an observed invoice in our interviews.
- Active bake-off thread: Small team picking between Vanta / Drata / Scytale is current buyer research, not a scored sample.
- Vanta as self-guided, Scytale as guided: A HackerNoon comparison from early September 2026 framed Vanta as a fast self-guided setup and Scytale as a guided one where an expert removes guesswork. That matches what our interviews said. It is still a third-party synthesis, not a substitute for a demo on your stack.
This is not a Glassdoor page
Glassdoor’s Scytale employer reviews are reviews of working at Scytale. This page reviews the compliance product. Scytale’s own CSM culture post is also about working there, not about buying the software.
Scytale vs Vanta for SOC 2
Vanta’s dated record shows 400 integrations and 2,665 G2 reviews. Scytale’s dated record shows 150+ vendor-confirmed integrations and 734 G2 reviews.
| Question | Scytale | Vanta |
|---|---|---|
| Website pricing | Quote-only; AWS Marketplace publishes a $7,500 floor for platform plus one framework | Quote-only; AWS Marketplace publishes scoped plan prices in our Vanta record |
| Expert in the default startup buy | Yes in Build DFY and Build Stronger; no in Build Starter | Software-led; you supply the compliance owner |
| Integrations (dated) | 150+ vendor-confirmed (August 11, 2026); G2 listed 99 on September 11, 2026 | 400 (July 24, 2026) |
| G2 (dated) | 4.8/5, 734 reviews (September 11, 2026) | 4.6/5, 2,665 reviews (July 24, 2026) |
| Native SCIM | Okta's catalogue lists SCIM create/update/deactivate; Scytale's pricing page does not name SCIM, so tier inclusion is unknown | Documented WorkOS-based SCIM in Vanta's Help Center; may require an upgrade or add-on |
Sources: software records for Scytale and Vanta. For the full Vanta product review, use Vanta review. For Drata's Audit Hub sample, use Drata review.
Is Scytale Worth It? How to Decide
Scytale fits a small team that will use the dedicated expert and can live with quote-based pricing, if a demo collected evidence from the systems you cannot replace. The users we interviewed were buying a first audit without a compliance hire. Run a bake-off when you already have that owner, the stack is unusual, or you need a public price. Scytale prepares evidence. It does not issue the SOC 2 opinion.
When Scytale Is a Strong Fit
- First SOC 2 without a GRC hire: A founder/CTO, an early-stage CEO, and a 10–30 person SaaS founder treated the consultant as the reason to buy.
- Standard cloud-native stacks: AWS, GitHub, and common identity or HR tools. A software engineer said the product stayed out of the way.
- ISO 27001 as a system of record: A head of InfoSec used policies, risks, controls, and evidence in one place.
- Cross-framework reuse: A GRC manager did not want to start over for the next certification.
When to Evaluate Alternatives (Run a Bake-Off)
- Connector breadth and review volume: Compare Vanta’s 400-integration record and 2,665 G2 reviews. See the Vanta review.
- Auditor workspace sample: Compare Drata Audit Hub. See the Drata review.
- Inspectable or self-hosted code: Compare Comp AI. See the Comp AI review.
- Unusual infrastructure: A DevOps engineer wanted exclusions and transparency around automated tests. Prove those in a proof of concept.
- You already have a compliance owner: Build Starter is the software-only SKU. Price it against other software-only quotes, not against DFY.
When to Skip Scytale
- You need a number on the marketing site today: scytale.ai/pricing will not give one.
- You will not use the expert and do not want to pay for one: Do not buy DFY or Stronger as a dashboard with a consultant attached by default.
- You expect the platform to issue SOC 2: Scytale cannot sign the opinion.
For the broader category, see the SOC 2 software guide.
Frequently Asked Questions About Scytale
How much does Scytale cost?
Scytale does not publish dollar prices on its own pricing page. AWS Marketplace listed the platform plus one framework from $7,500 for 12 months on September 11, 2026. Other starting dimensions on that listing are separate quotes. See the Scytale pricing guide.
Does Scytale include the SOC 2 audit?
No. Scytale is not the licensed CPA firm that issues the report. Some packages include auditor coordination, and AWS Marketplace lists a third-party audit service from $4,200 as a starting dimension. Confirm the firm’s identity, independence, scope, and complete fee.
Is Scytale better than Vanta?
Scytale belongs on the shortlist when you want a package that includes a dedicated GRC expert and can accept quote-based, per-framework pricing. Vanta may fit better when connector breadth, a larger independent review sample, or a software-led operating model matters more. This page does not replace the Vanta review.
Does Build Starter include a GRC expert?
No. Build Starter is the platform plus one framework, with no consulting plan listed. The dedicated consultant sits in Build DFY (LaunchReady, up to six months) and Build Stronger (StayReady, 12 months).
How long does SOC 2 take with Scytale?
Scytale does not guarantee a timeline. Vendor guidance in our July 24 source review gives 3 to 12 months to audit-readiness. Scope, control gaps, remediation speed, and the observation period agreed with the CPA determine the schedule. A Type II window is not something the software can compress.
What is Scy?
Scy is Scytale’s AI GRC agent. The current pricing matrix lists evidence review, gap scanning and remediation, governance, vendor intelligence, and questionnaire answering, with some functions limited by tier. Scytale does not publish deployment-specific accuracy. Test Scy on your own evidence and questionnaires.
What did Scytale users tell you?
Twenty-one current users named the dedicated GRC person, control-mapped evidence, and a first SOC 2 without a compliance hire. They asked for more exclusions on unusual infrastructure, fewer sync bugs, clearer onboarding, and better bulk workflow. Eighteen scored 5; three scored 4. Those are individual interviews, not a G2 sample.
Is this a review of working at Scytale?
No. This page reviews the compliance product. Glassdoor lists employee reviews of working at Scytale. If you searched for what it is like to work at Scytale, you are on the wrong page.
Final Verdict and Next Steps
Scytale collects evidence, maps it to controls, and, in the packages most first-time buyers want, puts a GRC expert on the account who already knows what the auditor will ask for. Buy it when that person is the reason you are paying, and when the connectors you depend on were demonstrated on your stack.
Price the quote-only subscription, the expert duration, and the CPA examination separately. Before you sign, pick Starter vs DFY vs Stronger in writing, demonstrate the connectors you depend on, and ask the CPA how they will use the auditor hub. Automated checks flag drift. They do not fix it, and Scytale cannot sign the SOC 2 opinion.
For CPA shortlists, use the SOC 2 auditor directory or request matches through find my SOC 2 auditor. For product facts, use the Scytale platform profile and the compliance tools directory.
How We Researched This Review
This is a product review for founders, engineering, and operations leaders assessing Scytale for SOC 2. Employer reviews of working at Scytale are out of scope. We have used Scytale ourselves and interviewed 21 current Scytale users (roles from founder and CTO to CISO, HR manager, DevOps engineer, and a regulated-startup founder; more interviews are in progress). Those conversations are quoted above; they are not a coded sample, and they do not mean every SKU, connector, or performance claim on this page was independently measured. We also compared Scytale’s public product, pricing page, and AWS Marketplace listing with our dated Scytale software record, the point-in-time G2 aggregate from September 11, 2026, and attributed discussions on r/SaaS and HackerNoon. Public homepage and pricing screenshots are vendor marketing captures, not tenant UI. Vendor marketing is labeled. Practitioner posts are individual experiences, not a representative sample.
More in Compliance Tools