 Menu
On this page
- Iru vs Vanta at a glance
- Can Iru compete with Vanta for a first SOC 2?
- Do Iru and Vanta fix device and identity failures?
- Where do Iru and Vanta differ beyond a first SOC 2?
- Is Iru or Vanta cheaper for the same setup?
- How do Iru and Vanta hand evidence to your CPA?
- What if you already use Iru Endpoint or Vanta?
- What should you test in both Iru and Vanta?
- Choose Iru, Vanta or neither
Iru and Vanta both organize SOC 2 controls, policies and evidence. Choose Iru if you also need device management, or Vanta if supplier reviews and risk management matter more. Iru's compliance product is newer: check completed audit references and your CPA's workflow.
Controls, policies and audit evidence
Applies supported device settings
When you need compliance and device management together.Newer compliance product: confirm completed audit references.
Controls, policies and audit evidence
Applies supported device settings
When you want to choose or keep separate IT tools.Supplier reviews and risk management: confirm the plan and add-ons.
Iru launched Compliance Automation when Kandji became Iru in October 2025. Your independent CPA signs the SOC 2 report. For the wider field, see SOC 2 compliance software compared by buyer fit. Read the Iru review and Vanta review for each product’s assessment, or the Iru profile and Vanta profile for sourced product details.
Iru vs Vanta at a glance
Iru and Vanta both manage compliance work. Iru also sells device and identity tools that operate some controls; Vanta connects to separately managed IT tools. The quote needs to cover both the compliance work and any operating tools you need.
| Criterion | Iru | Vanta | Evidence class |
|---|---|---|---|
| Core compliance work | Controls, tasks, policies, connected evidence and auditor collaboration; proposed control-text changes require approval. | Controls, policies, connected tests, a compliance roadmap and auditor collaboration. | Each vendor's own compliance product and help documentation |
| Compliance track record | Compliance Automation launched with Iru in October 2025. Ask for a completed audit reference using that product. | Founded in 2018 with a compliance-monitoring focus. Ask for completed audit references matching your proposed scope. | Company histories, not a measured comparison of audit outcomes |
| Device control | Endpoint Management can enforce supported settings; Compliance uses the resulting state. | Device Monitor observes settings; an MDM such as Iru manages device configuration. | Vendor product and help documentation |
| Identity lifecycle | Workforce Identity can provision supported business applications. Compliance-account SCIM remains unestablished. | SCIM manages Vanta accounts, roles and teams; a separate HR or identity integration maintains the People roster. | Vendor docs; distinct product scopes |
| Supplier reviews and risk register | Native supplier-assessment and risk-register workflows are not established in the reviewed Compliance documentation. | Documents supplier assessments and an organizational risk register; confirm required plan and add-ons. | Vendor product and help documentation; an unknown is not proof of absence |
| Frameworks and connected sources | SOC 2 and ISO 27001 are advertised; required cloud and custom-source fields need demonstration. | SOC 2 and ISO 27001 are advertised; required cloud and custom-source fields need demonstration. | Product pages and vendor documentation |
| General direct price | Personalized quote by products and user/device counts; no general dollar price published. | Personalized quote by plan and scope; no general dollar price published. | Direct pricing pages, September 30, 2026 |
| Auditor access | Actions, artifacts and comments; restricted auditor roles cannot view full control definitions. | Scoped auditor views and request lists; confirm the CPA's actual permissions and export. | Vendor permission and auditor documentation |
| CPA candidates in our directory | Confirm the intended CPA's Iru experience directly. | 41 attestation-capable firms list Vanta. | Directory listings; not proof of partnership, audit quality or evidence acceptance |
Product documentation checked September 30, 2026. The Vanta count points to firms to ask; it does not rank the products. We do not have an Iru-specific auditor list, so search the general directory and confirm the firm's experience.
Can Iru compete with Vanta for a first SOC 2?
Iru Compliance Automation and Vanta both organize controls, policies, tasks and evidence for an audit. Iru belongs on a first-platform shortlist even if you have never used Kandji. Device management adds to Iru’s appeal when you also need to secure a fleet.
Iru Compliance Automation describes tailored controls, assigned tasks, policy acknowledgements, connected-source artifacts and checks for evidence relevance and staleness. Native device and identity data can contribute, but cloud systems, business processes and manual records still need their own evidence paths. A secure fleet is one part of a SOC 2 program.
Vanta automated compliance describes prebuilt and custom controls, policy templates and employee acceptance, automated evidence collection, tests and an in-app compliance roadmap. Vanta also serves buyers starting from scratch; an existing compliance platform or MDM is not a prerequisite for choosing Vanta.
Iru’s Adaptive Compliance checks source and policy changes daily, proposes revised control or action wording, and records an administrator’s approval or rejection. It does not automatically fix a failed control, replace evidence attachments or change readiness calculations. Vanta advertises hourly automated tests and AI-assisted mapping of custom controls to tests. Iru’s wording updates and Vanta’s tests perform different jobs, so those schedules do not establish which platform collects evidence faster.
Iru introduced Compliance Automation in October 2025. Vanta began in 2018 with compliance monitoring, giving Vanta a longer history in this category. For a first-time buyer, Iru’s shorter product history calls for a relevant completed-audit reference and a demonstration of exceptions, policy revisions and CPA access. Ask Vanta for the same scope and outputs. With either platform, completed audit references should match your systems and the CPA access you need.
Do Iru and Vanta fix device and identity failures?
Iru Endpoint and Workforce Identity can apply supported device and application-access controls. Vanta’s Device Monitor records device state. If you need device management too, Iru can supply it alongside compliance; with Vanta, you choose the tool that applies those settings.
Iru’s SOC 2 page describes endpoint enforcement and native telemetry feeding compliance. Vanta’s Device Monitor guide describes checking encryption, screen lock and security software; it recommends an MDM for larger fleets needing policy enforcement and configuration management. An Iru Compliance quote must specify the Endpoint functions it includes. Include the tool that applies those settings in your Vanta budget.
Iru Workforce Identity provisioning uses outbound SCIM to create, update and remove accounts in supported applications. Vanta SCIM provisions access to Vanta itself, including roles and teams. Vanta’s People roster uses a separate HR or identity connection, and SCIM may require an upgrade or add-on. Vanta SCIM is not evidence that Vanta replaces Iru Workforce Identity across your business apps.
For a startup without device management, compare Iru’s compliance-plus-Endpoint proposal with Vanta plus the MDM you would otherwise buy. If identity management is also missing, price that scope separately on both sides. For an enterprise with established identity providers and MDM policies, Vanta may avoid a broader IT migration, while Iru must show what adopting its additional modules improves. The missing tools and required controls matter more than headcount.
Where do Iru and Vanta differ beyond a first SOC 2?
Iru and Vanta both support multiple frameworks. Vanta also documents supplier assessments and an organizational risk register. Those native workflows are not established in Iru’s Compliance documentation, so Vanta deserves a closer look if you want to review suppliers and manage risk in the same system.
Vanta Third Party Risk Management describes vendor inventory, intake and security reviews. Vanta’s assessment documentation says its Vendors page is available on all plans, but some assessment features require an add-on. Have the quote name the assessment functions and limits you need. Iru’s Compliance Automation page covers controls, tasks, policies and evidence. Iru’s Trust Center answers customers’ questions about your security; that is a different job from reviewing your suppliers.
Vanta’s separate Risk Management product documents a risk register, inherent and residual scoring, treatments and links to controls. Ask which of those functions your proposed plan includes. Iru can organize evidence for risk-related controls, but that does not establish a comparable native risk register.
For SOC 2 followed by ISO 27001, ask Iru and Vanta to show one reused artifact and one ISO-specific operating record. That shows which work carries over and which work is new. For a regulated business, add the permitted evidence types and data restrictions to that test. A HIPAA label is not permission to upload patient data; the Iru review’s data limits and Vanta’s terms FAQ explain the separate boundary to confirm in your agreement.
Is Iru or Vanta cheaper for the same setup?
Iru and Vanta both require personalized quotes, so their general pricing pages cannot tell you which is cheaper. Compare the total cost of compliance and any device or identity tools you need over the same term and control scope.
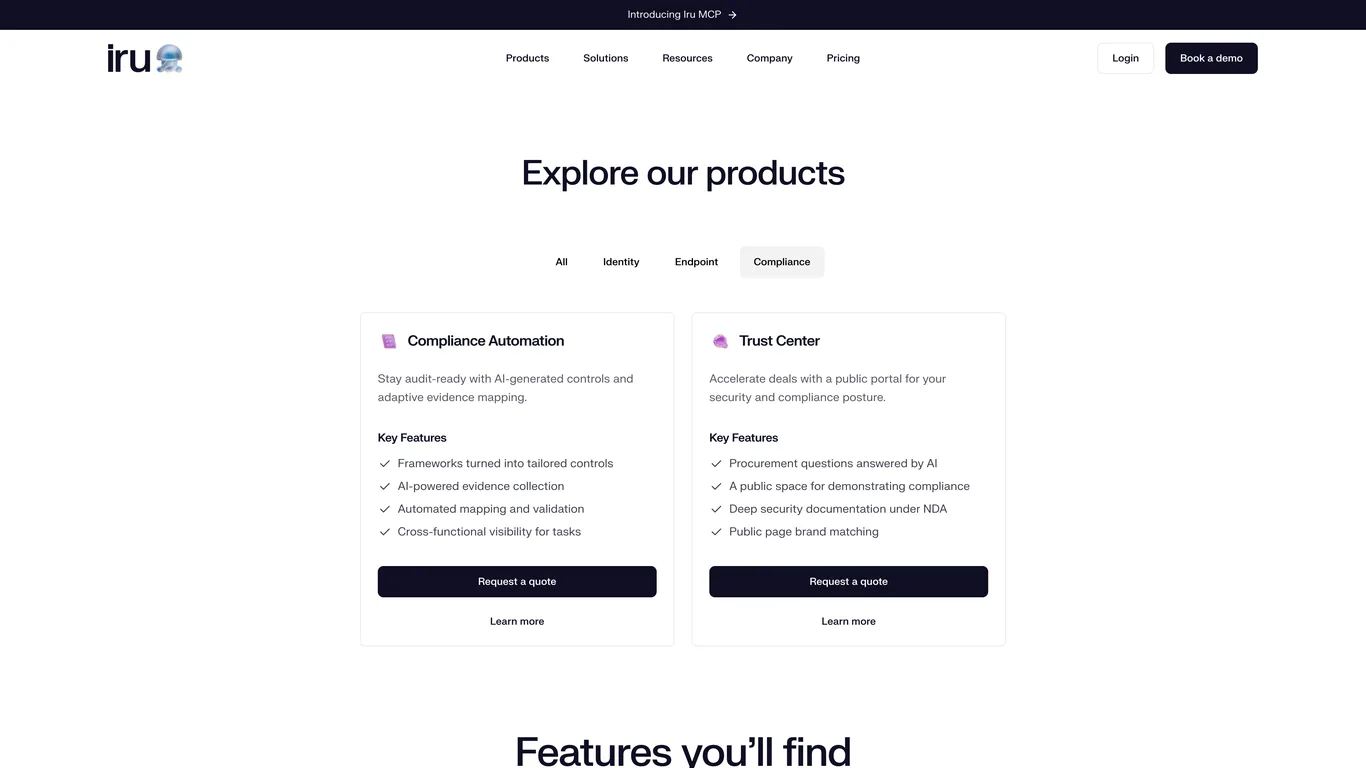
Iru’s startup bundle, checked September 30, starts at $9,000 per year on an annual commitment for up to 25 endpoints, 25 mobile devices and 25 identity users. It includes Endpoint Management, EDR, Vulnerability Management, Workforce Identity and Compliance Automation with Trust Center. Extra seats come in blocks of ten without a published added-seat price. This is a scoped startup offer, not a general Compliance Automation rate or a matched Vanta quote.
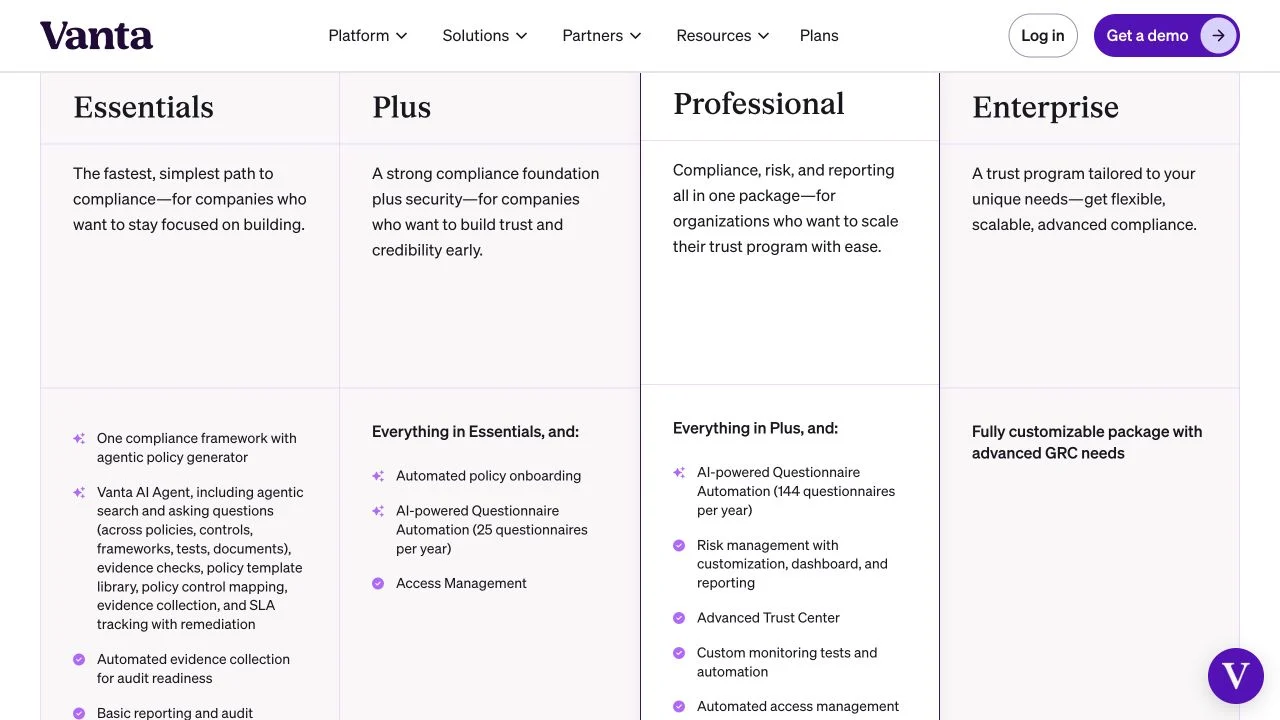
Vanta’s direct pricing page lists Essentials, Plus, Professional and Enterprise without dollar prices. Vanta’s observed contracts and channel offers have different buyer and package scopes; the Vanta pricing guide keeps those price types separate. They cannot establish a savings percentage against Iru’s startup bundle.
Ask for two totals over the same contract term: Iru Compliance plus the operating modules you need, and Vanta plus the device and identity tools you need. If those IT tools already run your business, include their continuing cost rather than treating it as a new Vanta fee. Include devices and users, frameworks, support deliverables, implementation, renewal terms, export rights and the CPA fee. Count a bundled tool as savings only if you need it and it passes your required controls.
How do Iru and Vanta hand evidence to your CPA?
Iru and Vanta both give auditors access to evidence. Iru’s restricted roles omit full control definitions; Vanta lets you scope the auditor’s view. Have your CPA try the actual permissions and export before the observation period begins.
Iru’s permissions matrix allows Auditor and Compliance Auditor roles to view control actions and artifacts, generate automated artifacts, assess relevance and comment. Those roles cannot view full control definitions, edit controls, connect sources, or upload or delete artifacts. Agree how your CPA will receive the definitions and retain evidence outside Iru.
Vanta documents auditor views and information request lists; either may require an upgrade or add-on. Confirm the package, then ask your CPA to open a selected control and artifact, request a missing item and retain an export. Confirm that your CPA will use the quoted workflow.
Our directory lists 41 attestation-capable CPA firms that say they work with Vanta. Treat the Vanta auditor list as a source of candidates, not proof of partnership or audit quality. We do not currently list a CPA firm with Iru Compliance experience. Search the SOC 2 auditor directory and confirm experience directly; a missing listing does not mean that Iru cannot be audited.
For a first Type II program, agree the observation period and evidence retention with the CPA before collection begins. If you are switching between Iru and Vanta, export control mappings, policies, artifacts, exceptions and request history; have the CPA assess historical continuity and any gaps before setting the cutover. Do not assume a switch either preserves or restarts the observation window automatically.
What if you already use Iru Endpoint or Vanta?
Iru Endpoint can manage your fleet while Vanta runs compliance. If you already use either product, this lets you keep device management and compliance separate.
Both vendors document the integration. Vanta’s connection guide specifies read-only Devices and Users access, optional Library reads for application metadata, an initial import and hourly sync. Vanta does not write device changes into Iru.
Vanta cannot detect XProtect through Iru, because Iru does not expose it as a detected application through the connector. Manual evidence must meet your CPA’s requirements. That does not establish whether Iru Compliance supplies the same signal natively; ask it to demonstrate the required evidence. Vanta’s public connector description names Apple devices, so Windows field coverage also needs a sample.
What should you test in both Iru and Vanta?
Give Iru and Vanta the same device, employee and control scope. Keep the evidence from both demonstrations with their quotes.
- Trace one device failure. On a test device, show a failed encryption or screen-lock control, who corrects the setting, and the resulting timestamped evidence. In Iru, identify the Endpoint and Compliance modules used. In Vanta, identify the MDM or Device Monitor path. Record the before-and-after artifact and owner; repeat on Windows if it is in scope.
- Run the compliance work. Publish and revise a policy, collect a test employee’s acknowledgement, and make a nonproduction evidence source stale. Show the alert, assigned owner, replacement artifact and retained history. Save the policy versions and exception record. In Iru, also distinguish an approved wording suggestion from a resolved exception; in Vanta, distinguish a passing test from approved policy work.
- Follow the same departing employee. Remove a test person’s access to one business application and to the compliance platform. Show the source identity event, application state, people record and approval history. Save those records and identify which product or external tool performs each action.
- Let the CPA work a sample. With restricted permissions, have the intended firm open the control definition or agreed substitute, inspect the artifact, ask a follow-up and retain an export. Keep its written assessment of access and file usability.
- Reconcile the quote and exit. Name every demonstrated product, module and licence quantity in the order, plus manual work, implementation, retained subscriptions, renewal and evidence-export rights. Save the itemized total and sample export before signature.
Choose Iru, Vanta or neither
Choose Iru
- You are buying a compliance platform and also need device management; Iru’s proposed modules cover both jobs without a separate MDM purchase.
- Iru demonstrates the required compliance workflow, fleet coverage and evidence, with a completed-audit reference relevant to your scope.
- Your CPA accepts Iru’s restricted view and the agreed route for definitions and exports.
Request the exact scope through Iru’s pricing page, then confirm experience with a firm from the auditor directory.
Choose Vanta
- You need Vanta’s documented supplier-review or risk-management workflows and have the required modules included in the quote.
- You will buy or retain separate device and identity tools, and Vanta collects the evidence your controls require from them.
- Vanta demonstrates the policy, exception and CPA workflow you need for your first audit.
Use the Vanta quote checklist, then shortlist CPA firms that list Vanta.
Choose neither
- You need someone to implement controls and answer audit requests, and neither software quote includes that work.
- Neither demonstration produces usable evidence for your critical custom systems, or neither proposal funds the manual work that remains.
Consider a separately scoped readiness provider or a different software model through the SOC 2 software buying guide and the software directory. Vanta alternatives lists replacements for Vanta, and Comp AI vs Vanta compares an inspectable or self-hosted route.
Vanta buyer guides
Start with the product record, then compare the review, pricing, alternatives, pair guides, and auditor listings before you shortlist.
More in Compliance Tools